INFORMATION SECURITY ASSURANCE
Information Security Management Software for Connected Operational Assurance
Centralised Simplicity Across Risks, Controls and Evidence
Zebsoft brings the organisational side of information security into one governed operating environment. Approved requirements become owned controls, scheduled activity, reviewable evidence, managed exceptions and decisions that leaders can trace back to source—without forcing every specialist security function into the same tool.
CENTRALISED SIMPLICITY
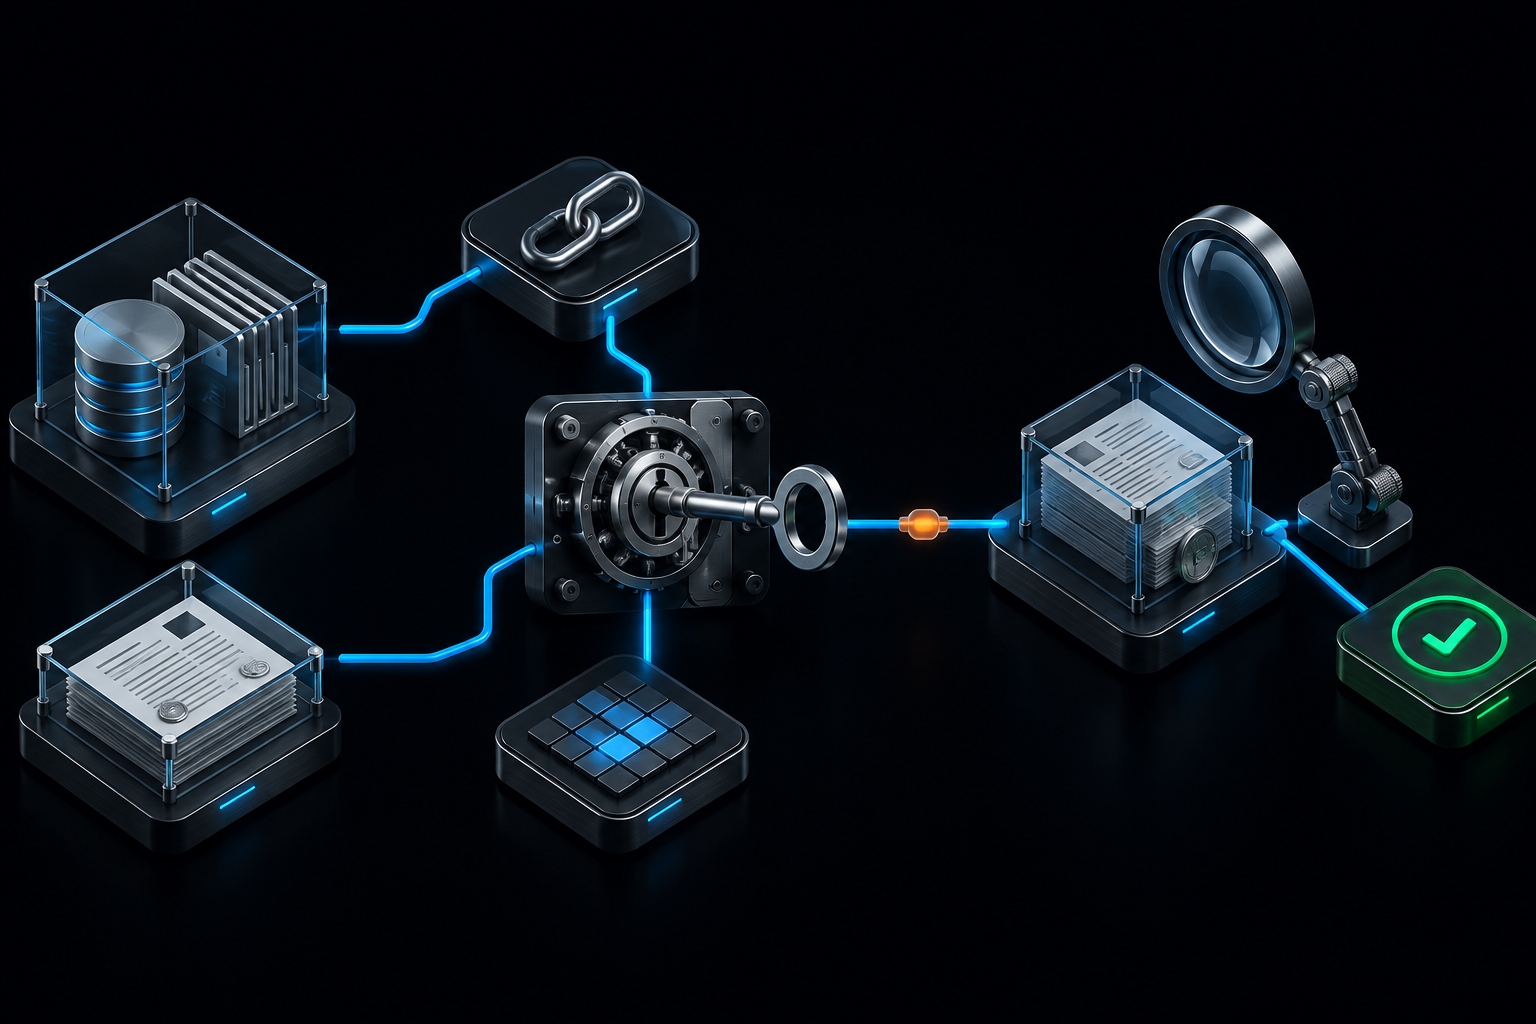
One Assurance Position Above the Tools That Already Protect You
Technical controls generate alerts, logs and protection. Compliance platforms automate evidence and framework monitoring. Policies describe intent. Zebsoft centralises the wider operating position—joining these inputs to accountable owners, controlled activity, human decisions and visible exceptions without pretending one system should replace every specialist tool.
Centralised simplicity does not mean placing every security activity inside Zebsoft. Endpoint protection should remain in the endpoint platform; access should be administered through the appropriate identity system; technical events should still be analysed by the security tools and people equipped to do so. Zebsoft provides the shared assurance context above them: why the control exists, who owns it, how its operation is reviewed, what evidence is sufficient, which exceptions remain, what action followed and who accepted the resulting risk. This reduces fragmentation without creating another technical system that teams must operate twice.
THE ZAP SECURITY ASSURANCE MODEL
Define, Communicate, Operate and Assure
Information security becomes operational when each important requirement can be understood, acted on and verified—not merely written into a framework.
AI Validation
Using AI in this process? Validate what matters.
AI can help prepare assessments, documents and recommendations. Before relying on the result, establish what needs checking, who is responsible and what evidence supports acceptance.
ZEBSOFT connects AI-assisted work to structured checks, competent review and recorded approval—helping you use AI with confidence.
THE CONNECTED SECURITY POSITION
Answer Five Questions Without Rebuilding the Evidence
Information security assurance depends on relationships. Zebsoft preserves those relationships so teams can move from the management question to the evidence behind the answer.
A central view should simplify relationships without flattening important distinctions. A technical test result is not the same as a competent review; a supplier certificate is not the same as validated performance; completing an action is not the same as proving effectiveness; and mapping a control to a framework does not decide whether the control is suitable for the organisation. Zebsoft keeps these inputs connected while preserving their different purpose, responsible person and required judgement. Leaders gain simplicity without losing the context needed to challenge weak conclusions, assign action or make an informed risk decision. This is how centralisation becomes useful assurance rather than a larger repository.
THE INFORMATION SECURITY LIFECYCLE
Keep Protection, Change and Assurance Connected
The security position changes as assets, people, suppliers, technology, threats and business priorities change. Zebsoft provides a governed route for that movement.
ASSET AND RISK CONTEXT
Know What Matters Before Selecting the Control
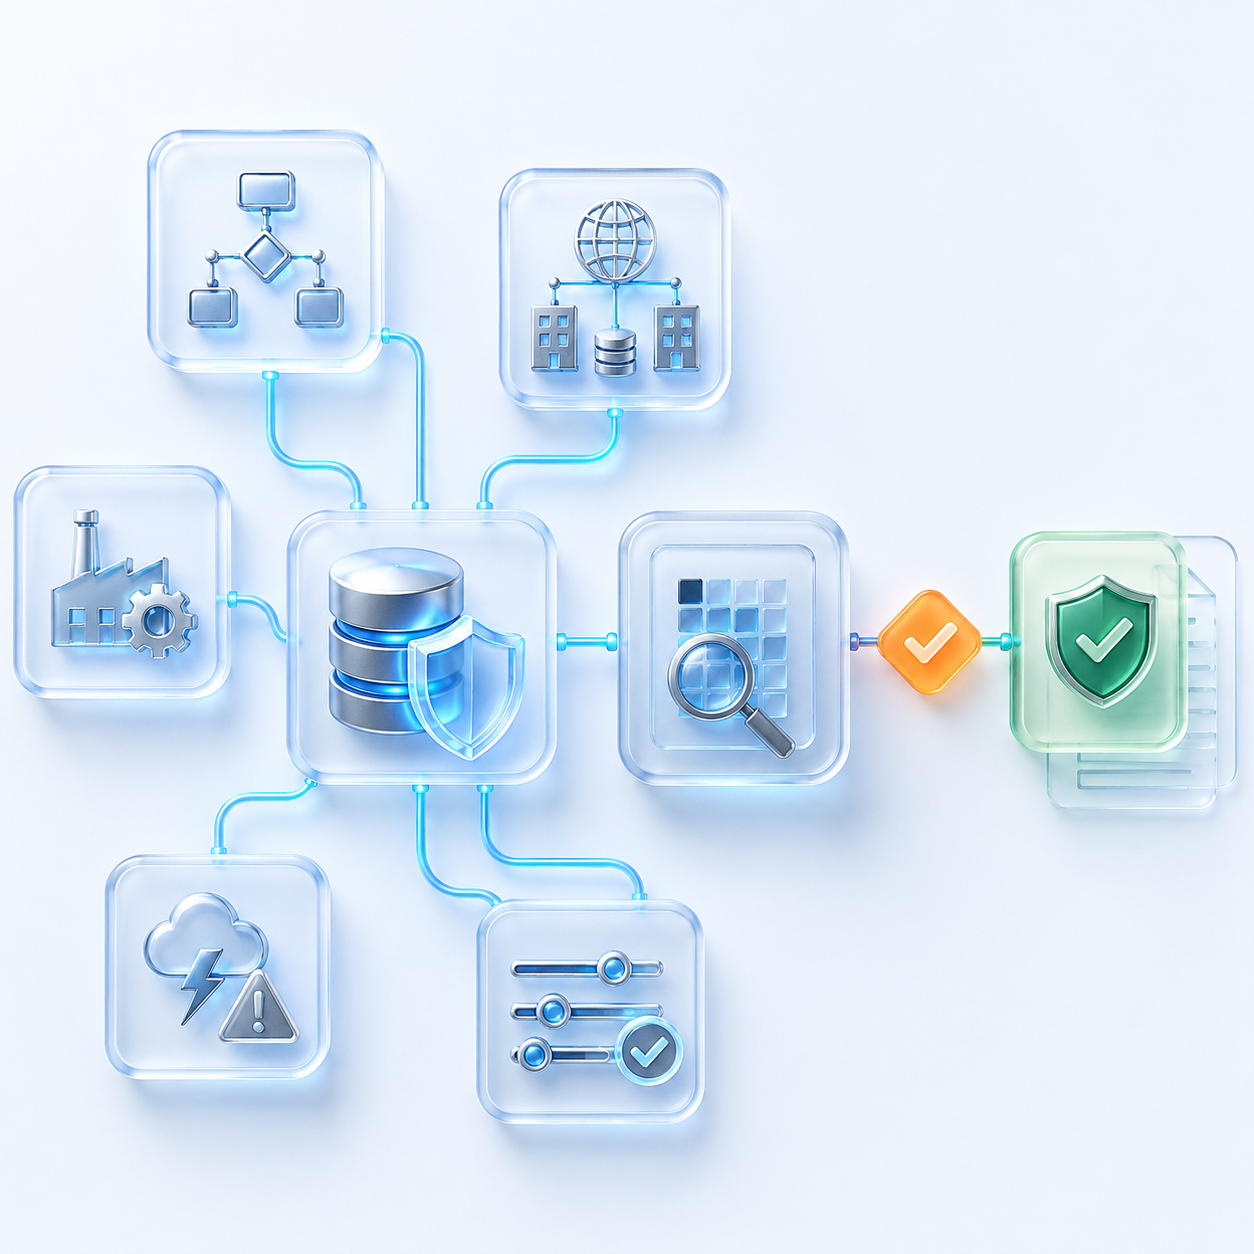
A security control has little meaning without context. Zebsoft helps connect the information being protected to the business activity it supports, the threats and dependencies affecting it, and the people authorised to make risk decisions.
Zebsoft structures the decision route. Competent people remain responsible for the risk method, evaluation and acceptance.
THIS IS HOW WE SOLVE THE PROBLEM
Preserve the Full Chain From Requirement to Verified Control
The evidence gap appears when policies, risk registers, technical tools, supplier reviews and audit findings all describe different parts of the same control. ZAP keeps the operational chain connected.
Requirement → asset and risk context → owned control → operation → evidence → human verification → exception or assurance
SUPPLIER AND THIRD-PARTY SECURITY
Assure the Dependency—not Just the Questionnaire
A supplier response is an input to assurance, not proof by itself. Zebsoft connects supplier criticality, evidence, validation, risk, conditions, actions and continued review to the information and services that depend on them.
OPERATIONAL CONTROL OWNERSHIP
Make Security a Managed Responsibility Across the Organisation
Information security is not operated by one team. Control owners, IT, procurement, HR, operations, legal, privacy specialists, suppliers and leaders each contribute different activity and judgement.
SECURITY UNDER CHANGE AND PRESSURE
Connect Incidents, Change and Resilience Back to Control
A control environment is most informative when something changes or fails. Zebsoft keeps the resulting learning connected to the risks and requirements it should improve.
Incident or change → affected asset and service → risk and control review → action and decision → test of the revised position
POSITIONED BEYOND COMPLIANCE AUTOMATION
Automation Collects Evidence. Operational Assurance Explains What It Means.
Leading compliance platforms have made automated evidence, continuous control monitoring, framework mapping and audit readiness expected capabilities. The Zebsoft competitive position is the centralised operational layer around them: configurable human and technical control execution, supplier participation, incidents, change, exceptions, approvals and accountable decisions.
| Buyer priority | Automation-led compliance platform | Zebsoft operational assurance domain |
|---|---|---|
| Primary strength | Connects to cloud, identity, device and development systems to automate tests, evidence collection and compliance status. | Centralises the operating system around assets, risks, controls, people, suppliers, incidents, actions and decisions. |
| Framework operation | Maps shared controls and automated evidence across security and compliance frameworks to accelerate audit readiness. | Lets one operational control support several requirements while each framework retains its own scope, testing, judgement and output. |
| Evidence position | Excels where evidence can be obtained and tested through integrations and repeatable compliance workflows. | Combines technical evidence with human reviews, supplier validation, incidents, change, approvals, exceptions and effectiveness decisions. |
| Operational flexibility | Provides a guided, automation-first route designed around recognised trust and compliance programmes. | Configures the organisation’s own routes, roles, stages, evidence, authority and escalation across technical and non-technical controls. |
| Buyer outcome | Faster compliance, continuous monitoring, streamlined audits and efficient external trust communication. | Centralised simplicity: one understandable assurance position above specialist systems, with every status traceable to accountable operation and decision. |
The choice is not automation or human judgement. Zebsoft makes both understandable within one controlled assurance position.
CONNECTED CAPABILITIES
Build the Information Security Domain From One Assurance Platform
The domain combines platform capabilities around a shared asset, risk, control and evidence context. Each area remains useful in its own right without becoming another isolated tool.
MANAGEMENT VISIBILITY
See the Position Behind the Status
Information security reporting should help leaders decide where confidence is justified and where further attention is required. A percentage without scope, evidence or exceptions can conceal more than it reveals.
Zebsoft supports interrogation of the position; it does not convert incomplete evidence into false certainty.
USE THE RIGHT INFORMATION SECURITY PAGE
The Domain Connects the Whole Position. Specialist Pages Go Deeper.
These pages support different buying and search intent. They should remain connected without repeating the same proposition.
A CONTROLLED TRANSITION
Move From Spreadsheets, Shared Folders or Another ISMS in Stages
Start with the information and relationships needed to establish a reliable current position. Do not migrate weak structure or unnecessary history simply because it exists.
Migration scope depends on source quality, required history, confidentiality, retention and the export or access methods available.
PRACTICAL QUESTIONS
Information Security Management Software FAQs
Security requirements, technology and legal duties vary by organisation and jurisdiction. Configure Zebsoft around the controls and decisions approved by competent people.
What is information security management software?
Information security management software helps an organisation govern how information risks, assets, controls, responsibilities, suppliers, incidents, actions and evidence are managed. Zebsoft connects those activities into an operational assurance system rather than treating them as separate records.
Is Zebsoft a cyber-security monitoring tool?
No. Zebsoft does not replace specialist technical tools such as endpoint protection, vulnerability scanners, identity platforms, firewalls or SIEM systems. It governs the requirements, ownership, reviews, exceptions, decisions and evidence surrounding those controls.
Does this page cover only ISO/IEC 27001?
No. This is the wider Information Security domain page. ISO/IEC 27001 and SOC 2 have a separate standards-focused page. Zebsoft can also support organisational, contractual and regulatory requirements defined by competent people.
Can one control support several requirements?
Yes. A real operational control may contribute evidence to several standards, contractual duties or internal requirements. Zebsoft can connect them while preserving the separate scope, judgement, testing and assurance output required for each framework.
Can supplier security be managed?
Yes. Supplier criticality, questionnaires, certificates, due diligence, risks, validation, actions, conditions and periodic review can be brought into the connected assurance position, with controlled external participation where configured.
Can we migrate from spreadsheets or another ISMS platform?
Yes. Registers, controls, SoA information, incidents, suppliers, actions and selected evidence can be mapped into a phased transition. Scope depends on source quality, required history and available export or access methods.
Does Zebsoft prevent security incidents?
No software can guarantee that incidents will not occur. Zebsoft helps organisations define and operate controls, identify exceptions, coordinate response, retain evidence and learn from events. Technical protection and competent security management remain essential.
Does the software guarantee compliance or certification?
No. Zebsoft supports an organisation’s management system and evidence. The organisation remains responsible for legal interpretation, risk acceptance, control decisions and compliance; an independent certification or assurance provider remains responsible for its own conclusion.
CENTRALISED SIMPLICITY. OPERATIONAL ASSURANCE.
Connect Control Operation to Organisational Assurance
Zebsoft brings assets, risks, controls, suppliers, incidents, evidence, exceptions and human decisions into one understandable, current information security position.