ACCOUNTABLE DATA GOVERNANCE
GDPR Management Software for Accountable Data Governance
Control the Controls—not the Personal Data
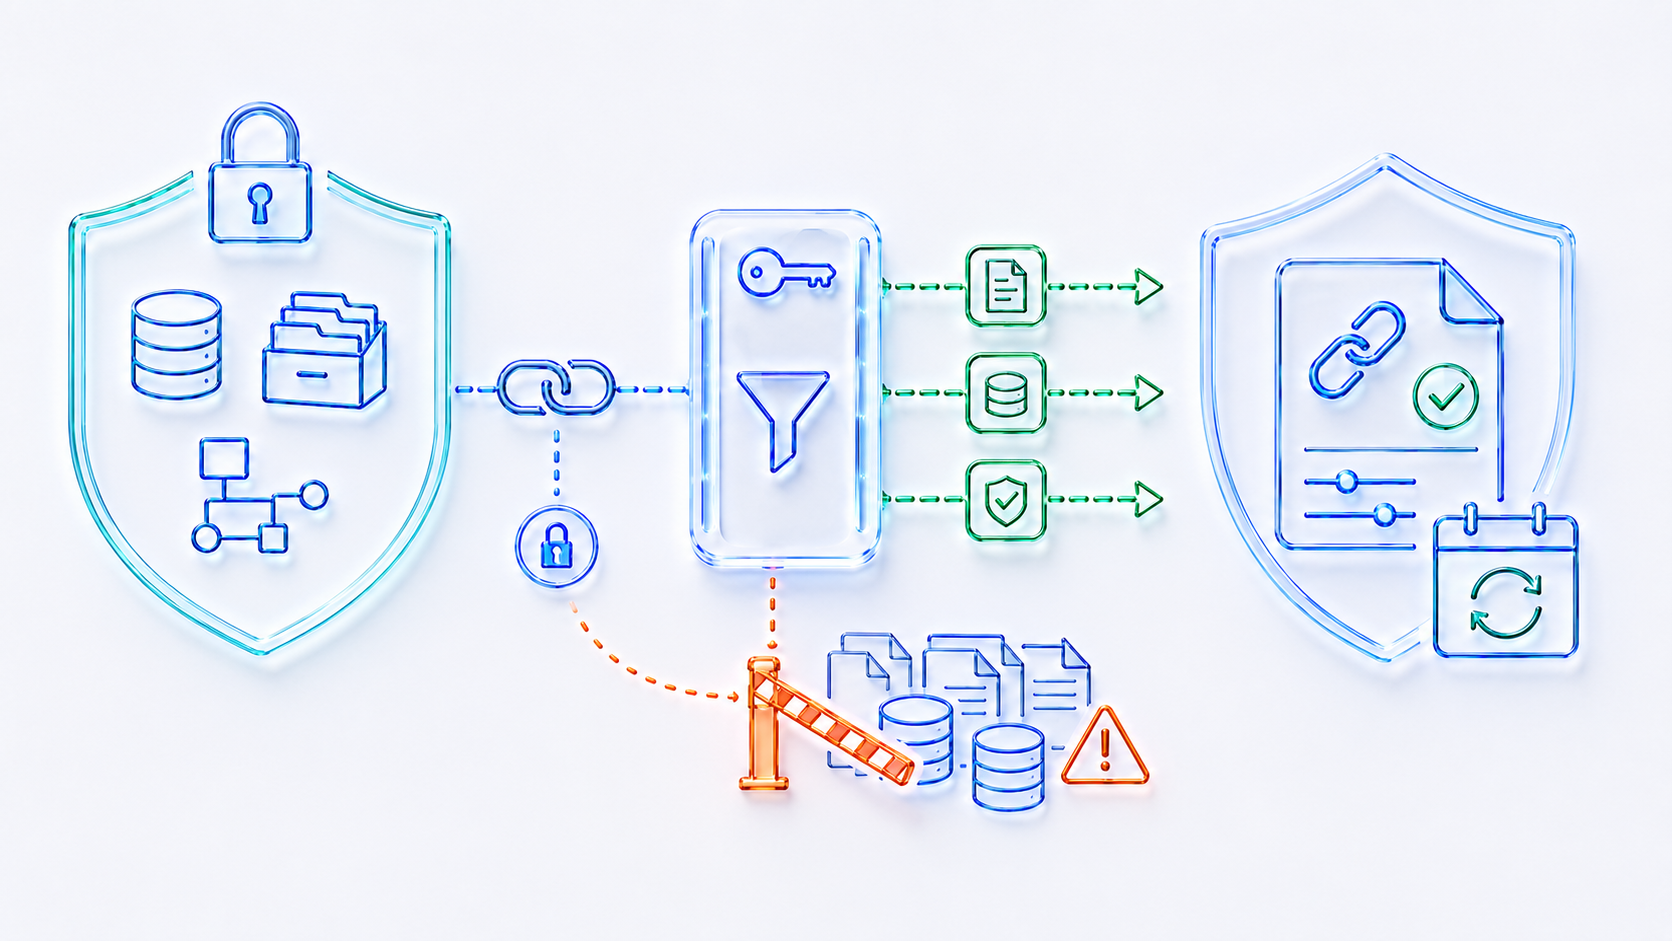
Zebsoft helps organisations define, operate and review the controls surrounding personal-data processing. It does not take control of the personal data held in HR, CRM, finance, email or operational systems.
Instead, configured workflows give each privacy requirement an owner, a decision route, required evidence, follow-up actions and a review point. The result is a more accountable way to manage RoPA records, DPIAs, rights requests, processors, retention decisions and breach response.
THE IMPORTANT DISTINC TION
Data Protection Depends on Controls That Continue to Work
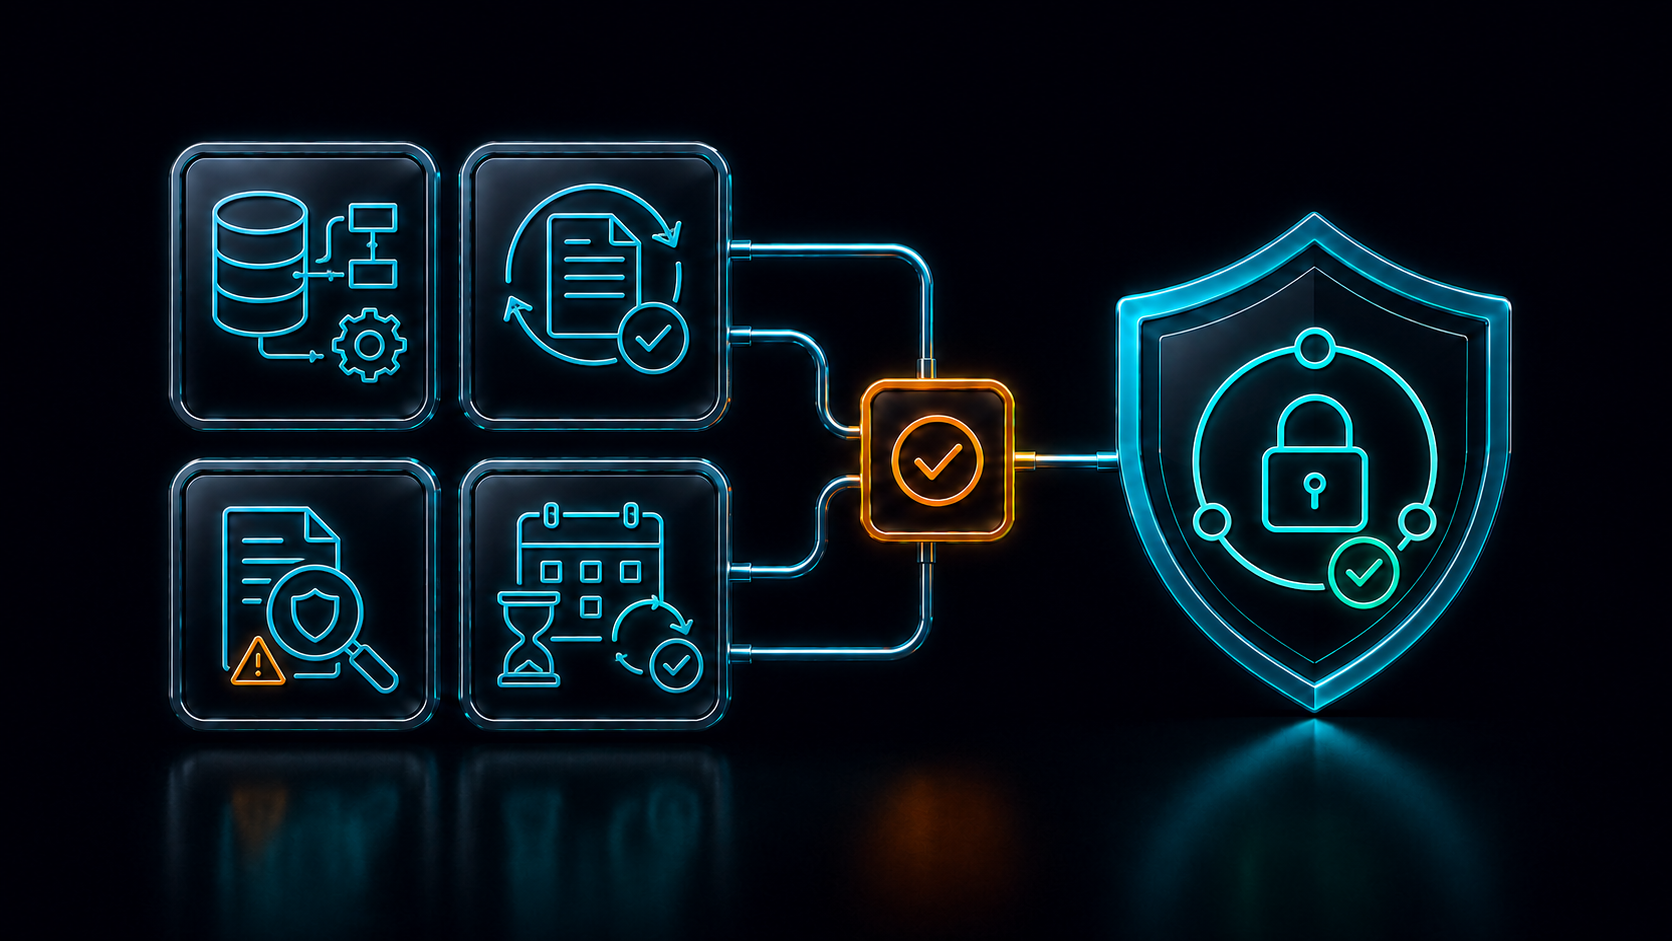
A privacy register may describe what should happen, but accountability depends on whether the organisation keeps that description accurate, applies the required safeguards, acts within relevant timescales and records its decisions. This is where workflow matters.
ZAP does not discover, secure or govern every item of personal data automatically. It helps the organisation control and evidence the human and procedural controls that should govern that data.
FROM REQUIREMENT TO ASSURANCE
The Privacy Control Chain
GDPR management software is useful when it turns a policy or legal requirement into a controlled operating route without pretending that the software makes the legal decision.
A REAL CON TROL WORKF LOW
From Proposed Processing to an Accountable Decision
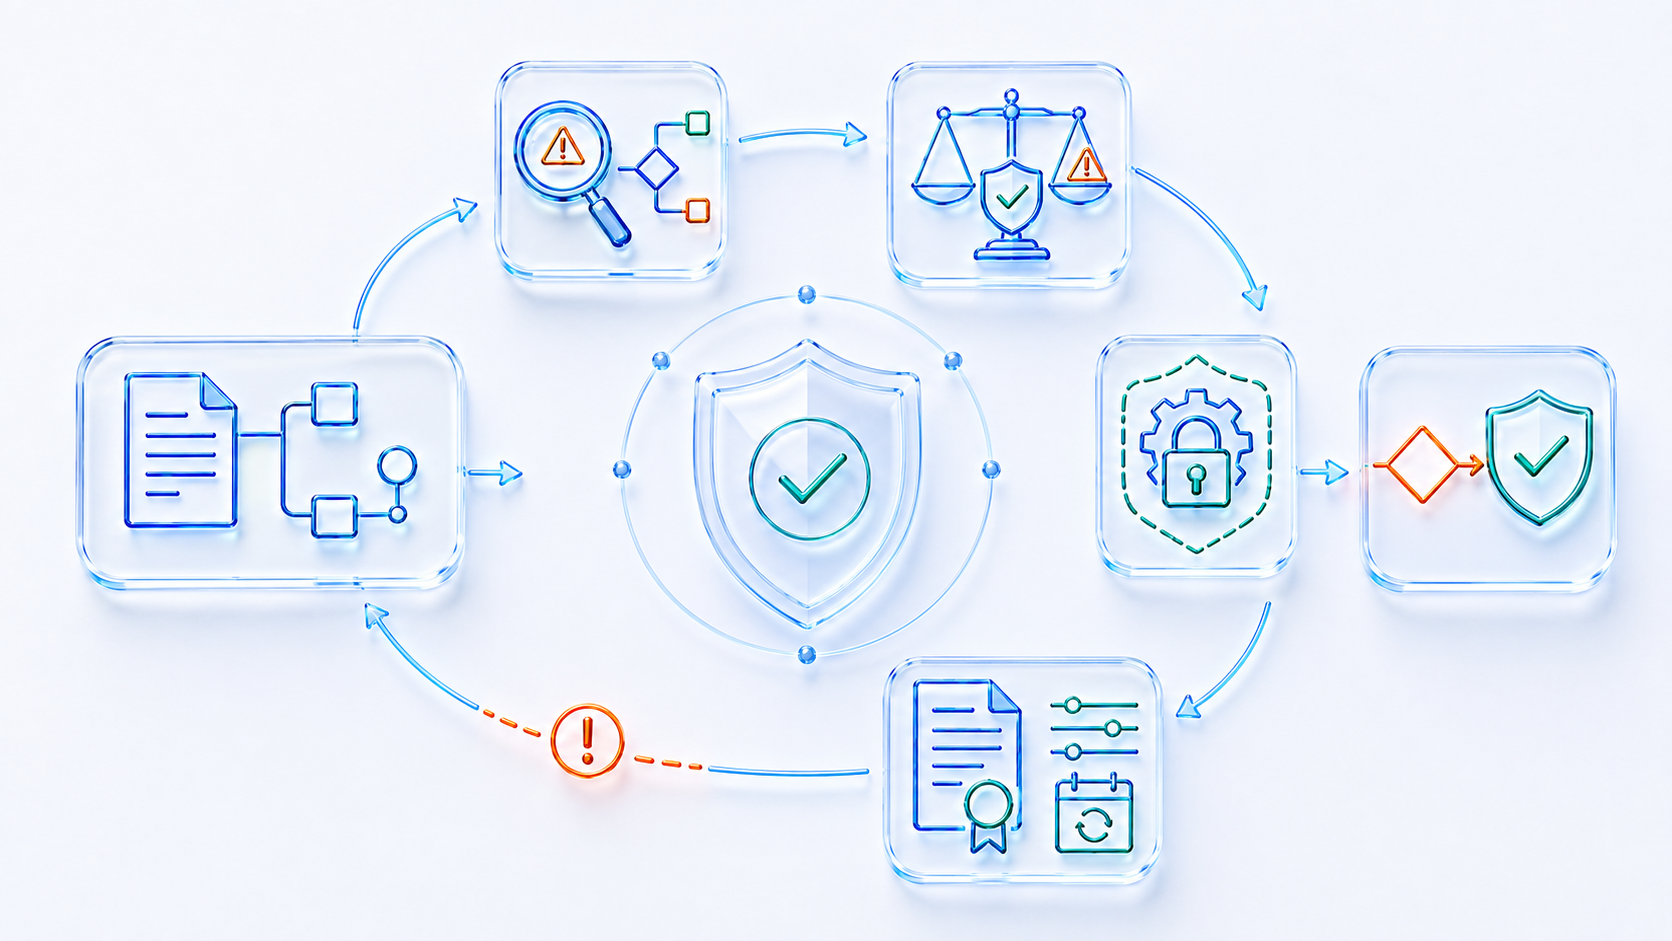
Consider a proposed new service, surveillance activity, AI use, data-sharing arrangement or system change. The privacy task is not simply to upload a completed DPIA document. The organisation must screen the activity, examine the risks, decide what safeguards are required and retain the basis of the decision.
A configured route can make missing steps visible. The organisation remains responsible for deciding whether processing may proceed and whether consultation with the ICO is required.
CONNECTED PRIVACY CONTROLS
Six Areas Where Workflow Strengthens Accountability
The existing page intent is retained, but each capability is expressed as a control process rather than an unsupported promise to manage all personal data.
RIGHTS REQUESTS IN PRACTICE
Control the SAR Response Without Treating It as a Ticket Alone
A subject access request can arrive through different channels and may require contributions from several systems and departments. The risk is not merely a missed diary date; it is an incomplete search, insecure disclosure, inconsistent redaction or a decision without an accountable basis.
ICO guidance currently requires a response without undue delay and generally within one month, subject to the specific rules on identity, clarification, fees and permitted extensions. The configured workflow should reflect the organisation’s procedure and current guidance.
INCIDENT TO ACCOUNTABLE OUTCOME
A Breach Workflow Must Support the Decision—Not Make It
Every known personal-data breach should be recorded. The organisation must assess the likely risk to individuals and determine whether notification is required. Where a breach is notifiable, current ICO guidance requires notification without undue delay and no later than 72 hours after awareness.
A timer can prompt urgency. It cannot determine the legal threshold, the risk to individuals or the content of a regulatory notification.
CONTROLLED GOVERNANCE, LIVE ASSURANCE
Apply the 70/30 Model to Privacy Management
Privacy governance contains a stable framework and a changing operational position. Both are required if a policy is to become an accountable system.
EVIDENCE WITH PROPORTIONATE DATA
Prove the Control Without Creating Another Privacy Risk
Privacy software should not become an uncontrolled copy of the personal data it is meant to help govern. The workflow should retain enough information to evidence the control while avoiding unnecessary duplication of identity documents, request bundles, investigation material or operational datasets.
The appropriate boundary depends on the organisation’s purpose, systems, risk assessment and data-protection procedure. It should be designed deliberately rather than created by convenience.
SOFTWARE SUPPORTS ACCOUNTABILITY
Clear Responsibility Is Part of the Control
Zebsoft can provide structured records, permissions, tracked activity, tasks, checklists, notifications, approvals and evidence routes. This is the practical role of GDPR management software. These features support privacy governance; they do not guarantee compliance or replace the controller’s, processor’s, DPO’s or legal adviser’s responsibilities.
The customer remains responsible for confirming that its configuration, procedures, permissions, training and use meet its own privacy obligati ons.
DEEPER GUIDANCE AND CONNECTED CONTROLS
Connect Privacy Governance to the Wider Management System
Privacy controls often depend on document control, risk, audit, supplier oversight and information security. Use these pages and primary sources to build the operational context around the GDPR workflow.
Current ICO guidance
COMMON QUESTIONS
GDPR Management Software FAQs
ZAP IT. KNOW I T. FIX IT.
Make Privacy Controls Visible, Accountable and Reviewable
Bring one real privacy process to a demonstration—such as a DPIA, RoPA review, subject access request, processor assessment or breach response—and see how ZAP can control its workflow without pretending to control the personal data itself.