Domains · Zebsoft Assurance Platform
Governing Operational Responsibility Across the Organisation
Give each area of responsibility a connected route from requirements to operational evidence.
A Domain is a long-lived area of organisational control. It brings together accountable owners, risks, obligations, operational activity and assurance within the Zebsoft platform.
Shared capabilities connect the work across Domains, helping responsible people see what needs attention and act with evidence.
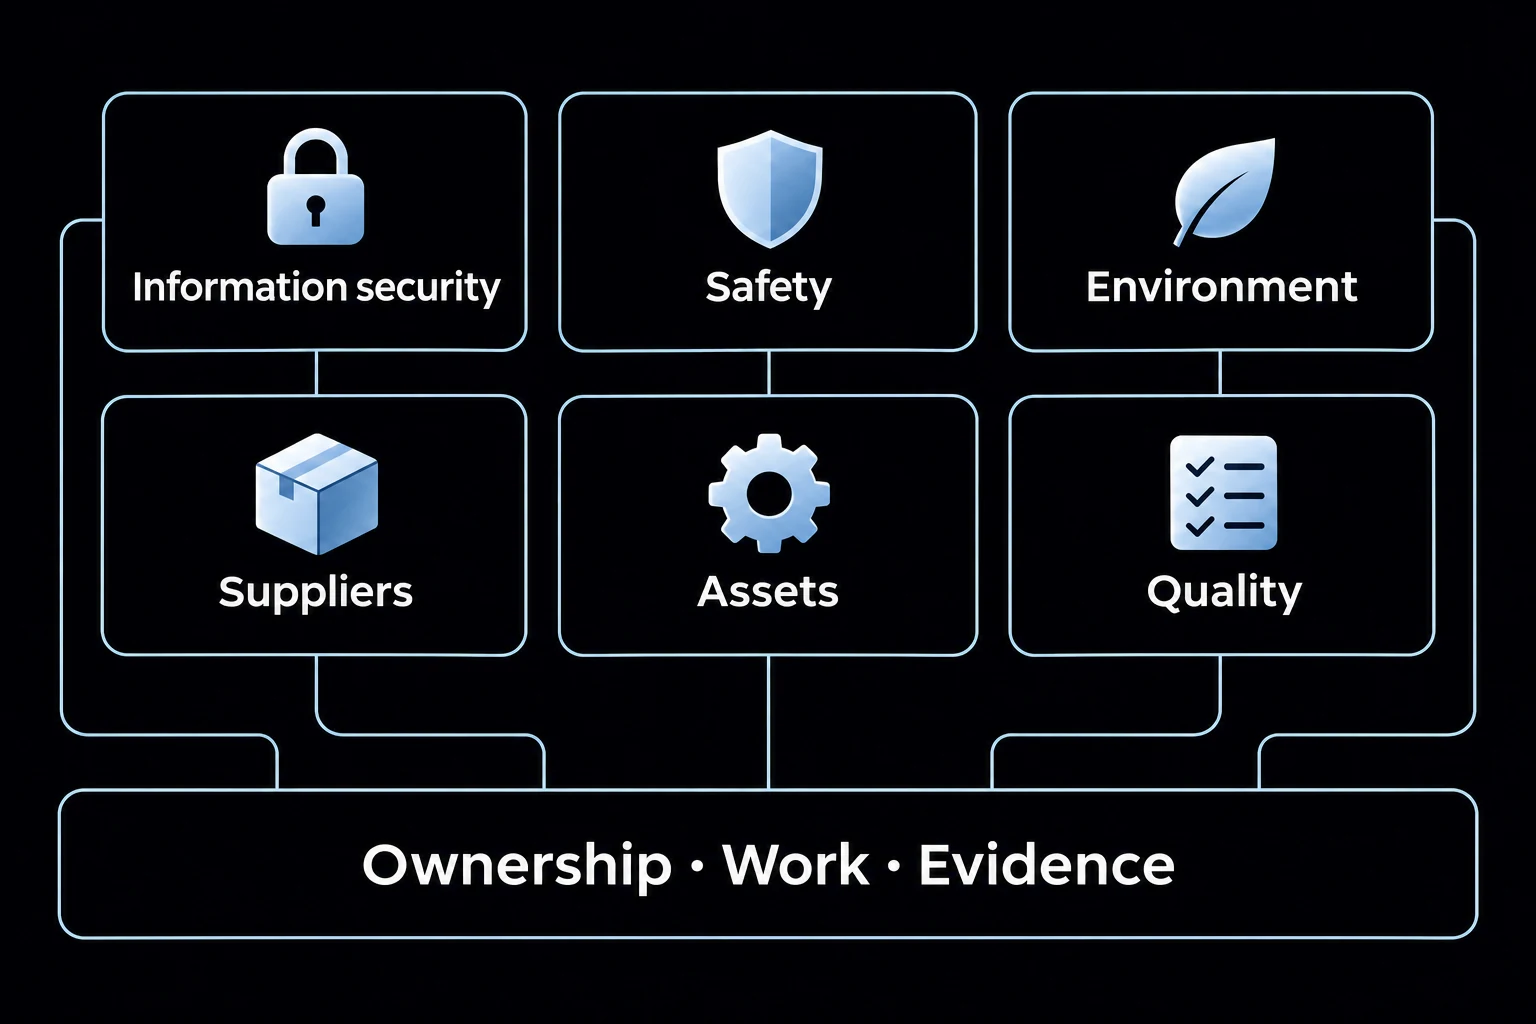
From responsibility to operational control
Make Ownership, Work and Evidence Clear
A Domain gives governance an operational context: what must be controlled, who owns it, how work is completed and what evidence supports a decision.
Define
Establish responsibilities, obligations, risks and expected controls.
Assign
Identify accountable owners and the people responsible for the work.
Coordinate
Connect documents, audits, checks, incidents and actions.
Validate
Review completed work, supporting evidence and exceptions.
Assure
Use findings and decisions to verify control and direct improvement.
Zebsoft organises the control route. People remain responsible for defining controls, judging evidence, approving change and owning compliance decisions.
One platform. Shared capabilities.
Different Responsibilities. Connected Ways of Working.
Domains describe the responsibility being governed. Capabilities provide reusable ways to carry out the work. Modules configure those capabilities for particular operational needs.
For example, the audit capability can support security reviews, workplace safety inspections, environmental audits and supplier assurance, with findings and actions linked to the relevant context.
Core governance Domains
Organise Control Around Real Responsibilities
Each Domain provides a context for its own requirements, controls, risks and assurance activity while sharing the platform’s capabilities, records and accountable workflows.
Information Security
Govern information assets, cyber risk, access and data protection responsibilities. Connect security requirements to the people, controls and evidence needed for review.
- Information asset ownership
- Security risks and controls
- Access reviews
- Incident and breach response
Health & Safety
Connect workplace hazards, safe systems of work and responsibilities with inspections, incidents, training and corrective action.
- Hazard and risk assessments
- Workplace inspections
- Incident investigation
- Competence and safe working
Environmental & Sustainability
Organise environmental responsibilities around aspects, impacts, obligations and operational controls, with evidence available for review.
- Environmental aspects and impacts
- Compliance obligations
- Operational monitoring
- Improvement actions
Supply Chain Integrity
Bring supplier, contractor and external-provider responsibilities into a controlled route for approval, evidence, monitoring and follow-up.
- Supplier approval and review
- Compliance evidence collection
- Supplier performance oversight
- External collaboration and actions
Asset & Infrastructure Integrity
Maintain oversight of physical assets, infrastructure, maintenance and operational reliability through connected ownership, records and checks.
- Asset registers and ownership
- Maintenance and inspections
- Lifecycle oversight
- Evidence of operational control
Operational excellence across every Domain
Quality and Improvement Connect the Whole System
Operational excellence is developed across Domains through shared processes, audits, corrective actions, objectives and performance review. Quality management and integrated management systems connect these activities around the organisation’s requirements.
Explore quality management → · Explore integrated management systems →
Defined requirements. Current evidence.
Connect Governance to What Actually Happens
Policies and registers establish expectations. Operational records show what occurred. Assurance depends on connecting both and giving exceptions to people able to respond.
Define the control
Keep the expected position clear and controlled.
- Policies, procedures and requirements
- Risks, obligations and controls
- Roles, responsibilities and objectives
- Review and approval requirements
Review the operational position
Use current activity and evidence to assess the result.
- Completed checks and supporting records
- Overdue, failed or incomplete activity
- Incidents, findings and linked actions
- Decisions and effectiveness reviews
A record alone does not prove effective control. Authorised people assess the relevance and reliability of the evidence, decide the response and verify whether it worked.
Domains & Shield levels
Scale Governance as Operational Complexity Grows
The Domain structure remains consistent. Shield levels support different scales of operation, depth of control and coordination.
Foundation Shield
Build structured governance in initial responsibility areas using core controls such as documents, audits, risks, incidents and actions.
Growth Shield
Extend across additional Domains with more coordinated operational activity, validation and assurance.
Enterprise Shield
Manage connected governance across multiple Domains, locations, teams and external stakeholders.
Domains explained
Common Questions
Is a Domain a department?
A Domain represents an area of organisational responsibility. Its controls and evidence can involve several departments, locations, suppliers or roles. Accountability remains explicit even when the work crosses organisational boundaries.
How do Domains differ from modules?
A Domain describes what is being governed. A module is a configured operational application, built from shared capabilities, that helps people complete particular work.
Can one capability support several Domains?
Yes. Audits, risks, document control, incidents and actions can operate across different responsibility areas. Each record retains its operational context, ownership and supporting evidence.
See the connected assurance structure
Start With the Responsibility You Need to Control
Bring a real governance challenge: a supplier evidence gap, a failed safety check, an overdue security review or an asset inspection. See how Zebsoft can connect the requirement, owner, activity, evidence and response.