ISO/IEC 42001:2023. AI GOVERNANCE THAT OPERATES. 

ISO/IEC 42001 AI Management System Software

Control AI Use, Risk, Impact and Accountability Across the Organisation

Zebsoft ISO 42001 software helps organisations establish, operate, evaluate and continually improve an Artificial Intelligence Management System (AIMS). It connects AI systems, purposes, owners, risks, impacts, controls, suppliers, approvals, incidents and evidence through accountable workflows.

The platform controls how governance work moves. It does not decide whether an AI system is acceptable, invent evidence or replace competent human judgement. 
  • Maintain a governed inventory of AI systems and use cases
  • Connect impact and risk assessments to controls and decisions
  • Route acquisition, development, deployment, change and retirement through approval
  • Monitor performance, incidents, supplier changes and emerging obligations
  • Support internal audit and independent certification without predetermining outcomes
ISO 42001 AI management system software for controlled AI governance risk impact and evidence

CURRENT POSITION CHECKED: 26 AUGUST 2026 

The AI Governance Position Has Moved On

A current AI governance programme must distinguish the management-system standard from impact-assessment guidance, certification rules and applicable law. These sources can reinforce one another, but they are not interchangeable. 


ISO/IEC 42001:2023

The current published AIMS requirements standard. It specifies what an organisation must establish, implement, maintain and continually improve when providing or using AI products or services. 


ISO/IEC 42005:2025

Current guidance for AI system impact assessments across the lifecycle, including foreseeable effects on individuals, groups and society. 


ISO/IEC 42006:2025

Requirements for bodies that audit and certify AIMS. It applies to certification and accreditation activity; it is not an implementation checklist for ordinary organisations. 


EU AI Act in enforcement

Enforcement powers and Article 50 transparency duties apply from 2 August 2026. Other high-risk obligations follow on the dates explained below. 

ISO/IEC 42001 certification does not by itself demonstrate compliance with the EU AI Act. Legal applicability depends on the organisation’s role, AI system, use, market, geography and other facts. 

A MANAGEMENT SYSTEM—NOT A PRODUCT CLAIM 

What ISO/IEC 42001 Does and Does Not Mean

ISO/IEC 42001 uses a management-system approach. It asks the organisation to understand its context, lead and plan the AIMS, support and operate it, evaluate performance and improve. The standard is designed to be applicable to organisations that develop, provide or use AI systems. 

What the standard provides

  • Requirements for establishing, implementing, maintaining and improving an AIMS
  • A framework for governing AI-related risks and opportunities
  • A lifecycle view of development, provision and responsible use
  • A basis for internal audit, management review and optional independent certification
  • Annex A control objectives that must be considered in context

What it does not provide

  • A guarantee that an AI system is safe, fair, accurate or lawful
  • A product certificate for every AI model or use case
  • Automatic compliance with the EU AI Act or other legislation
  • Permission to deploy an AI system without competent assessment
  • A substitute for legal advice, technical validation, human oversight or regulator decisions

THE OPERATING STRUCTURE 

Run Clauses 4–10 as One Connected AIMS

ISO/IEC 42001 follows the familiar management-system structure. The clauses should work together around real AI systems and decisions rather than exist as isolated policy documents. 


Context and scope

Identify internal and external issues, interested parties, legal and contractual requirements, organisational roles and the AI activities inside the AIMS boundary. 


Leadership and policy

Set direction, allocate responsibility, approve policy, provide resources and ensure AI governance is integrated into organisational processes. 


Planning

Address AI risks and opportunities, set measurable objectives, determine actions and manage planned changes to the AIMS. 


Support

Control competence, awareness, communication, resources and documented information needed to operate the AIMS. 


Operation

Plan and control AI lifecycle activities, conduct impact and risk work, apply controls and manage outsourced processes. 


Evaluation

Monitor, measure, analyse and evaluate performance; conduct internal audit; and complete management review. 


Improvement

Manage nonconformity and corrective action, learn from incidents and change, and continually improve AIMS suitability and effectiveness. 

KNOW WHICH AI YOU GOVERN 

Build a Usable AI System Inventory

An AIMS cannot govern an AI estate that nobody can describe. The inventory should cover internally developed systems, third-party services, embedded AI features, general-purpose models, automated decision support and approved employee uses.

Zebsoft relates the inventory to ownership, affected parties, suppliers, risks, assessments, obligations, controls, incidents, changes and evidence. 
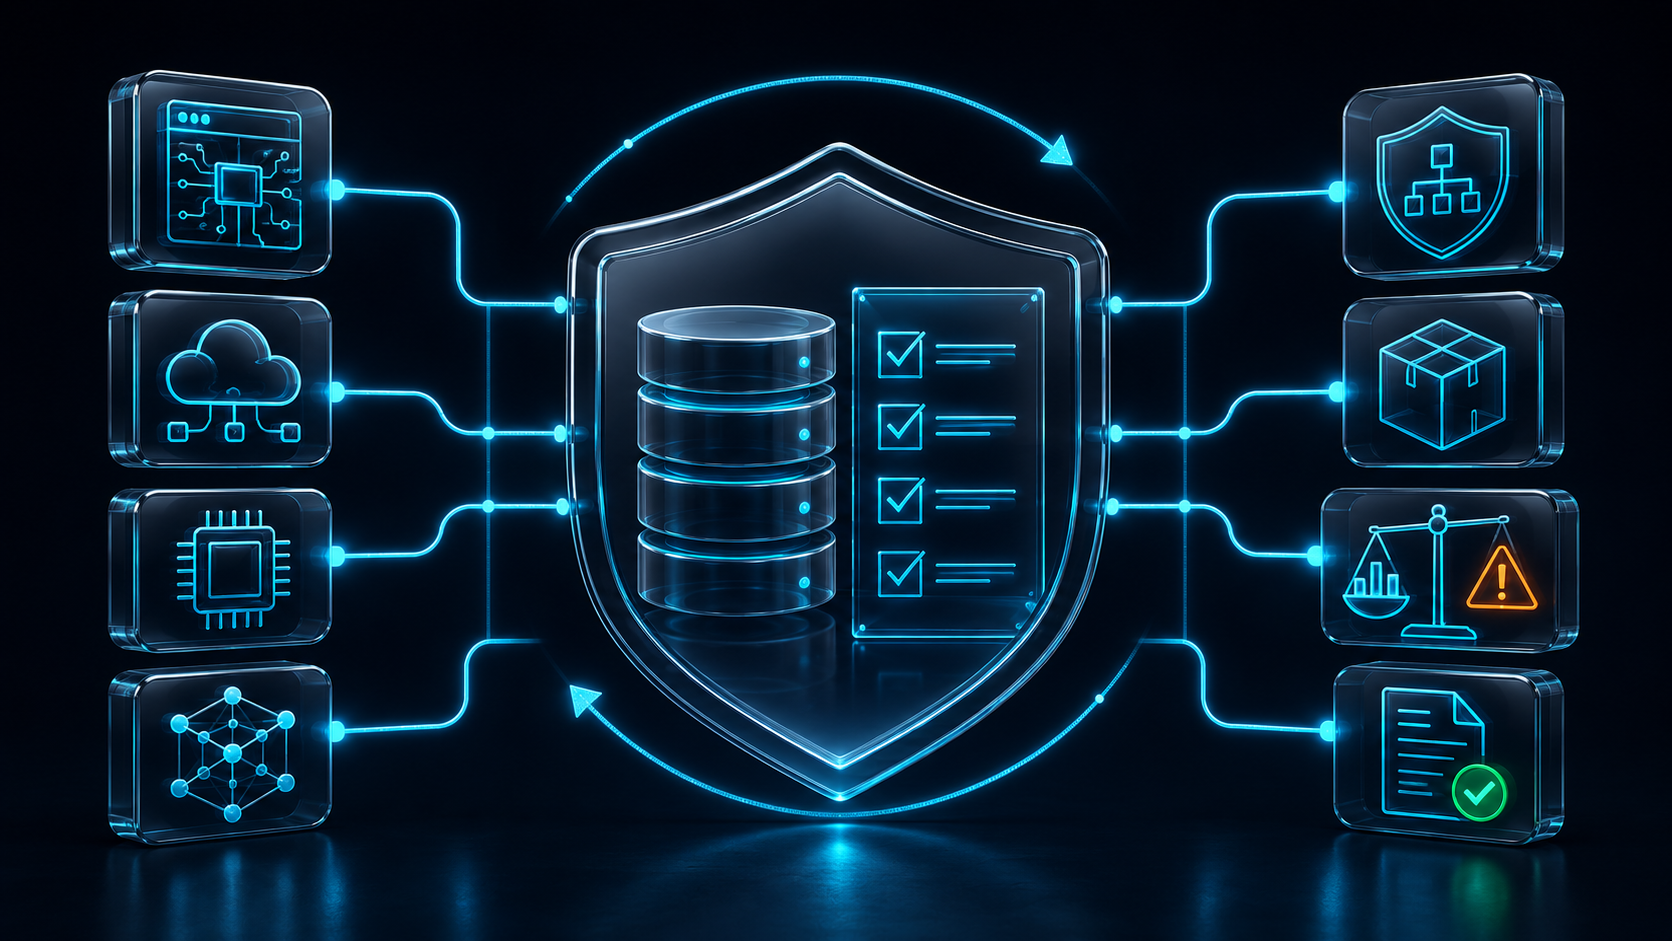
  • Business purpose, intended outcome and prohibited or excluded use
  • Provider, developer, deployer and other relevant organisational roles
  • Model, service, data sources, interfaces and dependent systems
  • Users, affected people, customers and other interested parties
  • Geographic reach, applicable obligations and contractual commitments
  • Lifecycle state, accountable owner, approval status and next review
  • Known limitations, monitoring needs and change triggers
AI system inventory connecting owners suppliers risks controls impacts approvals and evidence

ASSESS EFFECTS BEFORE AND DURING USE 

Connect ISO/IEC 42005 Impact Assessment to AI Risk Management

ISO/IEC 42005:2025 provides lifecycle guidance for assessing foreseeable impacts on individuals, groups and society. ISO/IEC 23894:2023 provides guidance on AI risk management. Zebsoft can connect both forms of analysis to the AIMS without pretending they are the same exercise. 


Define the use context

Describe intended purpose, users, affected people, operating environment, foreseeable misuse, dependencies and decision significance. 


Identify impacts and risks

Record beneficial and adverse effects, uncertainty, affected groups, failure modes, misuse, bias, privacy, safety, security and operational concerns. 


Evaluate and treat

Apply approved criteria, determine controls, assign owners, record residual exposure and route risk acceptance to authorised people. 


Review through change

Reassess when the model, data, provider, use, population, law, performance or operating environment changes materially. 

The system preserves inputs, reasoning, evidence, consultation, assumptions and approvals. Competent people determine assessment conclusions and whether the remaining risk and impact are acceptable. 

CONTROL THE COMPLETE AI LIFECYCLE 

Govern the Decision Route From Proposal to Retirement

AI governance fails when approval is treated as the end of the process. Models, data, suppliers, usage and legal expectations change. The control route must continue while the system is in use. 

01 

Propose

Record the need, intended use, accountable sponsor, expected benefit, affected parties and initial constraints. 

02 

Assess

Classify the system and complete proportionate impact, risk, privacy, security, safety and legal assessment. 

03 

Validate and approve

Test against defined criteria, review evidence and limitations, record conditions and obtain authorised human approval. 

04 

Deploy and monitor

Control access and use, communicate instructions, collect evidence, watch performance and route exceptions or incidents. 

05 

Change or retire

Reassess significant changes, withdraw approval when required, manage records and dependencies, and confirm controlled retirement. 

GENERATIVE AI NEEDS OPERATING CONTROLS 

Move Beyond a Generic AI Acceptable-Use Policy

A policy can state expectations, but it cannot prove how specific tools and uses are approved, monitored and changed. Generative AI requires controls around information, output, human review, disclosure and provider dependency. 


Approved tools and uses

Define which services, models, integrations and use cases are permitted, restricted or prohibited and who may use them. 


Information boundaries

Control whether personal, confidential, customer, regulated, export-controlled or intellectual-property material may be entered. 


Grounding and provenance

Require authorised sources, preserve relevant inputs and references, and distinguish retrieved facts from generated language. 


Human review

Define competence, review depth, validation and approval before AI-assisted output influences operations, customers or public information. 


Transparency and marking

Apply disclosure, labelling or machine-readable marking where the organisation’s role, content and applicable law require it. 


Supplier and model change

Monitor terms, training-data commitments, hosting, retention, security, capabilities, limitations and material model updates. 

EU AI ACT: CURRENT ENFORCEMENT TIMELINE 

Do Not Use an Out-of-Date 2024 Implementation Timeline

The EU AI Act entered force on 1 August 2024 and applies progressively. As of 26 August 2026, enforcement powers and Article 50 transparency duties are active. The organisation must determine its own role and which provisions apply. 


2 February 2025

Prohibited-practice rules, relevant definitions and AI literacy obligations began applying. 


2 August 2025

Governance rules and obligations for general-purpose AI models began applying. 


2 August 2026

Enforcement powers and Article 50 transparency obligations began applying, subject to the Act’s detailed scope and limited transitional provisions. 


Later high-risk dates

Annex III high-risk rules apply from 2 December 2027; rules for high-risk systems embedded in regulated products apply from 2 August 2028. 

Zebsoft can map applicable duties to owners, controls, evidence, reviews and actions. It cannot determine legal classification without the relevant facts or replace competent legal and regulatory interp retation.

UK AI GOVERNANCE 

Map Existing Law and Regulator Expectations

The UK continues to apply AI requirements through existing law and a regulator-led, sector-specific approach rather than a single horizontal equivalent of the EU AI Act. 

Depending on the use, duties may arise from data protection, equality, employment, consumer, safety, medical-device, financial-services, competition, intellectual-property, cyber-security and contractual requirements. The ICO’s AI and data-protection guidance remains important where personal data is involved.

Zebsoft gives each obligation an owner, interpretation record, control route, evidence requirement, review date and change history.

CROSS-BORDER OPERATIONS 

One AI System Can Have Several Governance Contexts

The same AI service can create different responsibilities where the organisation develops it, provides it, deploys it, imports it, distributes it or uses its output. 

AIMS scope should therefore connect each system to markets, users, affected people, contracts, sector rules, data flows and responsible legal entities. Governance must also distinguish a global minimum control from local requirements.

Do not label the entire AI estate “EU AI Act compliant” because one process or supplier is controlled. Record the system, role, provision and evidence actually assessed.

THIS IS HOW WE SOLVE THE PROBLEM 

Put a Controlled Route Around Every Important AI Decision

Most organisations already have AI policies, risk templates, supplier questionnaires and project approvals. The weakness is that the controls are separated from the systems, people and changes they are meant to govern. 

The governance problem

AI enters through many routes. Procurement, software updates, embedded features and employee tools can bypass a central register. 

Assessments become documents. Risk and impact conclusions are not linked to approval conditions, owners or monitoring.

Controls rely on follow-up. Reviews, supplier evidence, testing and actions live in email, spreadsheets or SharePoint.

Changes break prior assumptions. A model, provider, data source or use changes while the old approval remains visible.

Assurance becomes reconstruction. Teams assemble proof after a customer, auditor, regulator or incident asks for it.

How Zebsoft solves it

Define the control. Set scope, trigger, responsible roles, required inputs, decision criteria, time limits and evidence. 

Communicate the requirement. Route current policy, conditions, restrictions, training and changes to authorised users and owners.

Operate the workflow. Require assessment, testing, approval, monitoring, incident response and change review at the right lifecycle point.

Assure the result. Connect dashboards and reports to current evidence, exceptions, human decisions, audit findings and management review.

Escalate what does not conform. Overdue work, control failure, unexpected performance and unauthorised use enter accountable action routes.

AI FOR AUTHORISED INTERROGATION AND ANALYSIS 

Use AI to Understand Governed Information

ZAP AI can help authorised users interrogate approved records, summarise current information and surface relationships or patterns that require attention. 

  • Find systems, risks, impacts, controls, obligations and evidence
  • Compare recurring incidents, exceptions and assessment themes
  • Surface overdue reviews, missing relationships and change triggers
  • Summarise current approved records for a competent reviewer
  • Support questions only across information the user is authorised to access

HUMANS REMAIN RESPONSIBLE 

Do Not Generate Bogus AI Governance Evidence

Zebsoft does not use AI to invent policies, risks, impact assessments, control operation, evidence, approvals, conformity conclusions or certification decisions. 

  • Leadership defines scope, policy, objectives and risk appetite
  • System owners describe purpose, use, limitations and operating context
  • Competent specialists assess impacts, risks, law, security, safety and performance
  • Authorised people approve deployment, change, risk acceptance and retirement
  • Auditors and certification bodies evaluate evidence and reach independent conclusions

Humans remain responsible for the decisions, work, approvals and consequences. AI may assist analysis; it does not acquire organisational accountability.

CERTIFICATION READINESS 

Operate the AIMS While Preserving Certification Independence

ISO/IEC 42006:2025 sets additional requirements for bodies that audit and certify AIMS. Zebsoft can help the organisation prepare and present controlled evidence, but certification remains an independent conformity-assessment decision. 


Define scope and roles

Confirm the organisational boundary, AI activities, sites, legal entities, products, services and accountable governance structure. 


Operate and retain evidence

Run the AIMS long enough to demonstrate genuine inventory, assessment, control, monitoring, audit, review and improvement activity. 


Evaluate internally

Complete internal audit and management review, address nonconformities and verify corrective-action effectiveness. 


Support external assessment

Provide authorised records while the certification body determines samples, findings, competence needs and the certification conclusion. 

Zebsoft does not certify organisations and cannot guarantee certification. It helps responsible people demonstrate how the AIMS is controlled, operated, evaluated and improved. 

CONNECT GOVERNANCE WITHOUT COLLAPSING INTENT 

Integrate AI Governance With Security, Privacy, Quality and Risk

An AIMS can share organisational processes with other management systems, but each standard and legal duty retains its own scope, criteria and evidence. 


ISO/IEC 27001

Connect AI assets, access, suppliers, incidents, vulnerabilities and information-security risk without treating security as the whole of AI governance. Explore ISO 27001 software. 


Privacy and GDPR

Relate personal-data use, lawful basis, DPIAs, rights, retention and processors to relevant AI systems and decisions. Explore GDPR software. 


Enterprise risk

Connect AI risk to business, operational, safety, security, regulatory and supplier contexts. Explore risk management software.


Quality management

Use controlled design, supplier, validation, nonconformity, corrective-action and improvement processes where AI affects products or services. 


ISO/IEC 38507:2022

Use governance guidance to help governing bodies enable and direct the effective, efficient and acceptable use of AI. 


ISO/IEC 23894:2023

Use AI risk-management guidance to strengthen the way AI-specific risk is integrated into organisational activities and functions. 


NIST AI RMF

Where useful, map the voluntary NIST AI Risk Management Framework and its Generative AI Profile without presenting them as legal or ISO certification requirements. 

MOVE FROM POLICY PACKS TO OPERATING GOVERNANCE 

Migrate Without Losing Ownership, Evidence or History

Zebsoft can replace or connect fragmented spreadsheets, SharePoint lists, policy folders, ticketing tools and supplier files. Migration should improve control, not merely copy old disorder into a new database. 

01 

Discover

Locate inventories, assessments, policies, approvals, suppliers, incidents, actions, evidence and unofficial AI use. 

02 

Clean

Remove duplicates, identify obsolete records, resolve uncertain ownership and preserve required history. 

03 

Map

Relate source fields and evidence to the new system structure, lifecycle states, controls and responsibilities. 

04 

Validate

Check completeness, permissions, relationships, workflow, reporting and representative migrated records. 

05 

Cut over

Approve the new source of truth, communicate responsibilities, retire superseded routes and monitor adoption. 

The migration plan can be phased by AI risk, business unit or lifecycle state. Live high-impact systems and imminent regulatory duties should not wait behind low-value historical cleanup. 

CONTROLLED EVIDENCE 

Make AI Governance Verifiable From the Work Itself

A customer, auditor, regulator or governing body should be able to follow a reported position back to the system, assessment, control, evidence and authorised human decision. 


AI governance activity Fragmented approach Zebsoft controlled operation
AI system inventory A spreadsheet with uncertain ownership and status Each system has a purpose, owner, role, provider, lifecycle state, affected parties and linked obligations
Impact and risk assessment A one-off document prepared before approval Assessment conclusions, assumptions, controls, owners, evidence and review triggers remain connected
Deployment decision Informal sign-off in email or a project meeting Named competent people review defined criteria, record conditions and retain an authorised decision
Supplier or model change Updates are discovered after behaviour or terms change Change triggers reassessment, testing, approval, communication and monitoring
Assurance Evidence is reconstructed for audit or customer review Dashboards and reports trace to current records, exceptions, decisions and human accountability

PRACTICAL QUESTIONS 

ISO 42001 AI Management System Software FAQs

Use the licensed standards, current regulator information and competent professional advice when determining exact requirements. 

What is ISO/IEC 42001:2023?

It is the current international requirements standard for establishing, implementing, maintaining and continually improving an Artificial Intelligence Management System. 

Does Zebsoft certify an AIMS?

No. Zebsoft supports implementation, operation, evidence, audit and improvement. An independent competent certification body reaches the certification decision. 

Is ISO/IEC 42005 part of ISO/IEC 42001?

It is a separate 2025 guidance standard for AI system impact assessment. It complements ISO/IEC 42001 and can strengthen the organisation’s impact-assessment method. 

Does every AI system need the same controls?

No. The organisation determines proportionate controls from context, use, effects, risk, obligations and lifecycle stage. It must consider relevant Annex A control objectives and justify its approach. 

Can we govern third-party and embedded AI?

Yes. The inventory and supplier processes can cover hosted tools, models, APIs and AI embedded in wider products, with controls reflecting the organisation’s actual role and influence. 

Does ISO 42001 certification prove EU AI Act compliance?

No. Certification can support structured governance and evidence, but legal compliance depends on the applicable provisions and facts of each organisation and AI system. 

Which EU AI Act dates matter now?

Article 50 transparency duties and enforcement powers began applying on 2 August 2026. Annex III high-risk rules apply from 2 December 2027 and regulated-product high-risk rules from 2 August 2028. 

Can AI complete our governance records?

AI may help authorised users interrogate and analyse approved information. Humans remain responsible for assessments, controls, evidence, approvals, interpretations and decisions. 

Can we integrate ISO 42001 with ISO 27001?

Yes. Common processes can be connected while the AIMS and ISMS retain their own scope, specialist requirements, risks, controls and audit conclusions. 

Where can we verify the current position?

See the official ISO/IEC 42001 page, ISO/IEC 42005 page, ISO/IEC 42006 page, the European Commission AI Act enforcement timeline, the NIST AI RMF and current ICO AI guidance. 

BRING ONE REAL AI USE CASE 

See How Zebsoft Makes AI Governance Operable and Verifiable

Choose a real system—generative AI, decision support, automated inspection, customer interaction, workforce use or an embedded supplier feature. We will show how purpose, ownership, assessment, controls, approval, monitoring, change and evidence remain connected.