ACCOUNTABLE DATA GOVERNANCE 

GDPR Management Software for US Teams

Coordinate Privacy Controls Across US and International Operations

ZEBSOFT helps US teams coordinate GDPR governance where it applies to their operations. Connect processing records, privacy assessments, requests, vendors and incident decisions through configured workflows, with accountable owners and evidence of review.

Instead, configured workflows give each privacy requirement an owner, a decision route, required evidence, follow-up actions and a review point. The result is a more accountable way to manage RoPA records, DPIAs, rights requests, processors, retention decisions and breach response. 
  • Define which privacy controls should apply and who owns them
  • Communicate decisions, tasks and deadlines to the responsible people
  • Retain evidence showing whether the control operated as intended
  • Review exceptions and changes before records become outdated
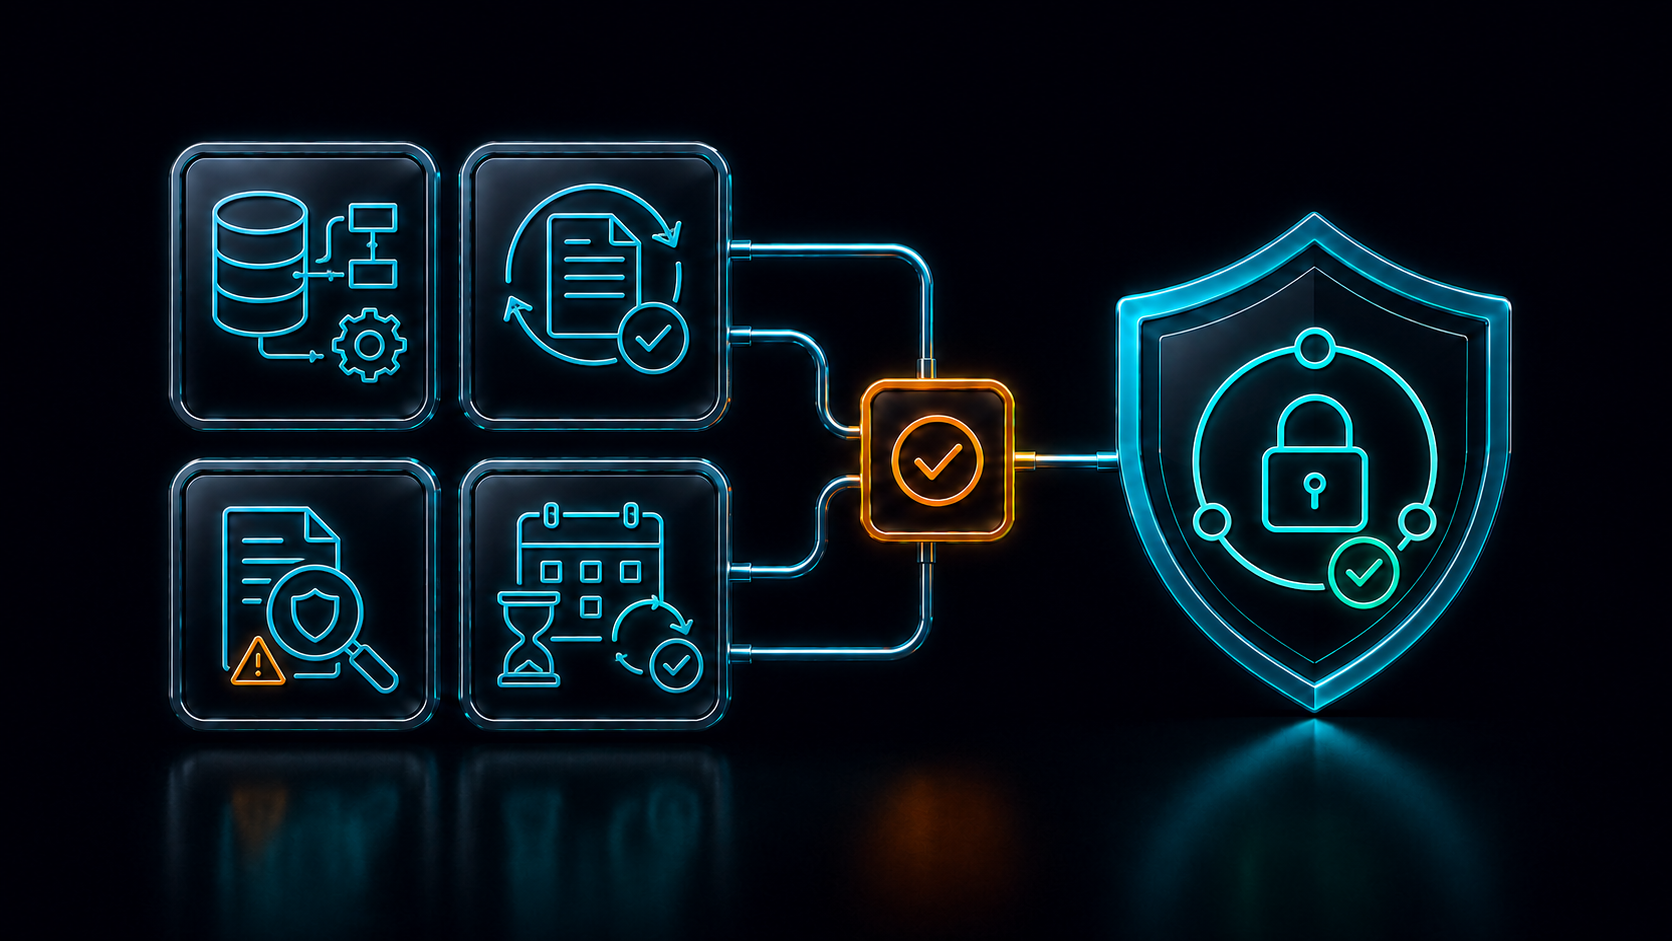
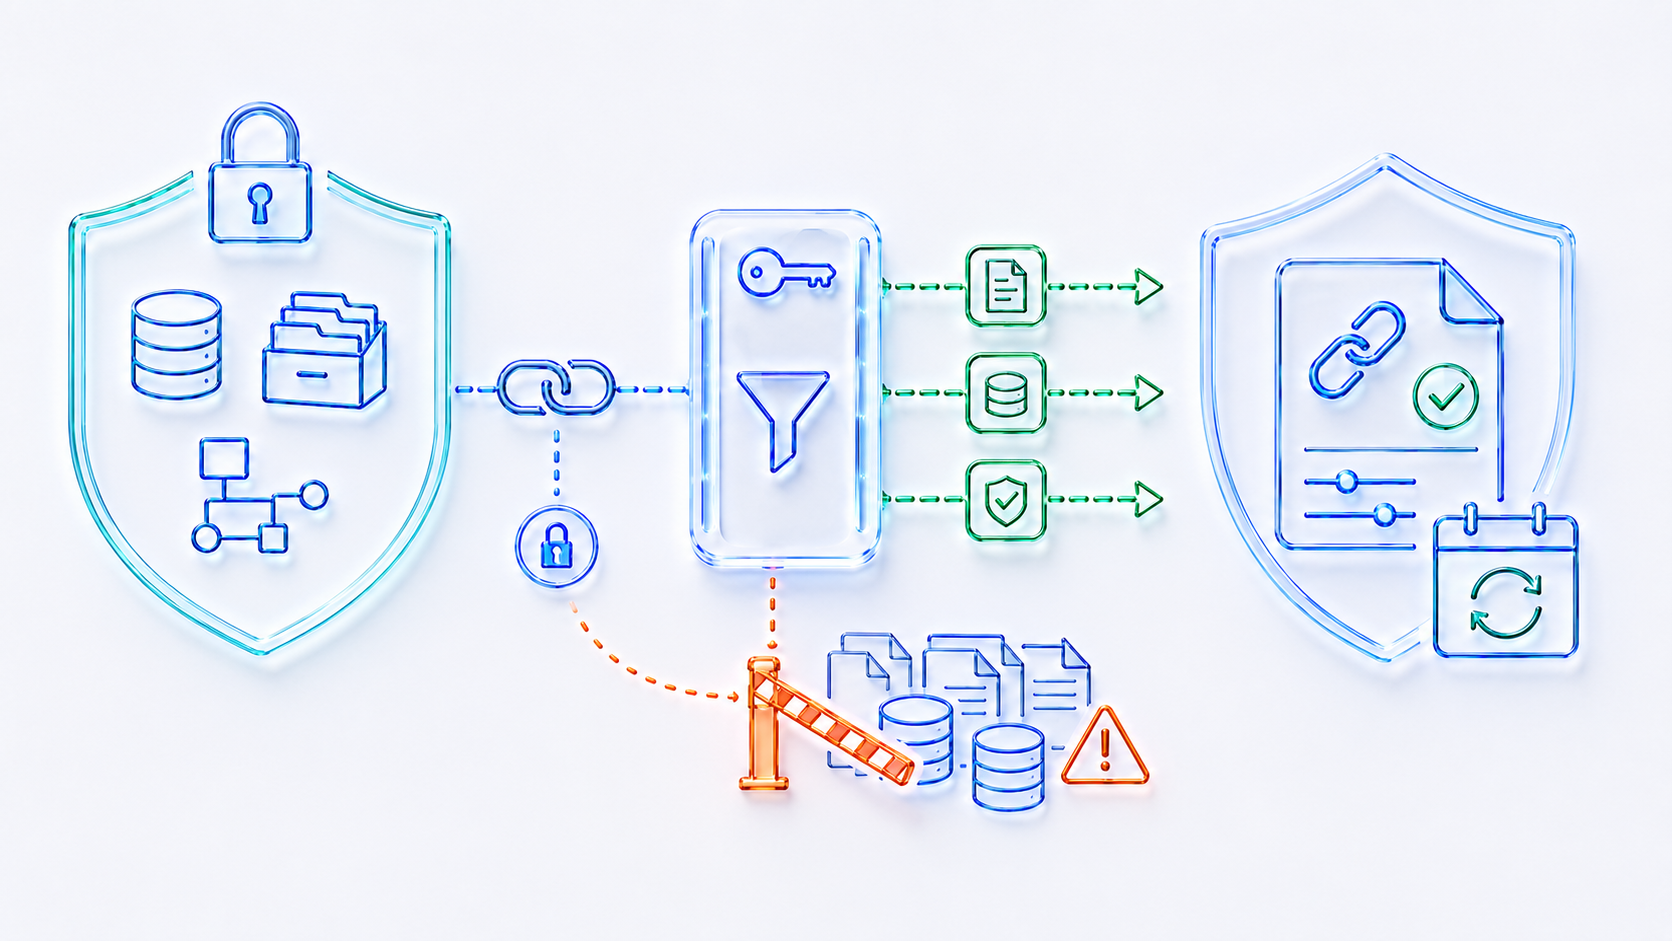
GDPR governance controls surrounding business data systems through accountable workflows

THE IMPORTANT DISTINCTION

Establish Where GDPR Applies to Your US Business

Being based in the United States does not automatically place a business outside GDPR. EU GDPR can apply to processing connected with an EU establishment, or to offering goods or services to people in the EU or monitoring their behavior there. UK GDPR has its own territorial scope. Have qualified specialists assess your activities and record the applicable duties. Read the European Commission guidance. 


The data

Source personal data can remain in your operational systems. Governance records and attachments may themselves contain personal data, so apply suitable access, security and retention controls to those records too.


The control

The control defines what people must do: identify a lawful basis, review retention, assess risk, approve sharing, respond to a request or evaluate a breach. 


The assurance workflow

ZAP records ownership, routes the required review, captures supporting evidence, assigns follow-up and retains the decision history so gaps remain visible. 

ZAP does not discover, secure or govern every item of personal data automatically. It helps the organization control and evidence the human and procedural controls that should govern that data. 

FROM REQUIREMENT TO ASSURANCE 

The Privacy Control Chain

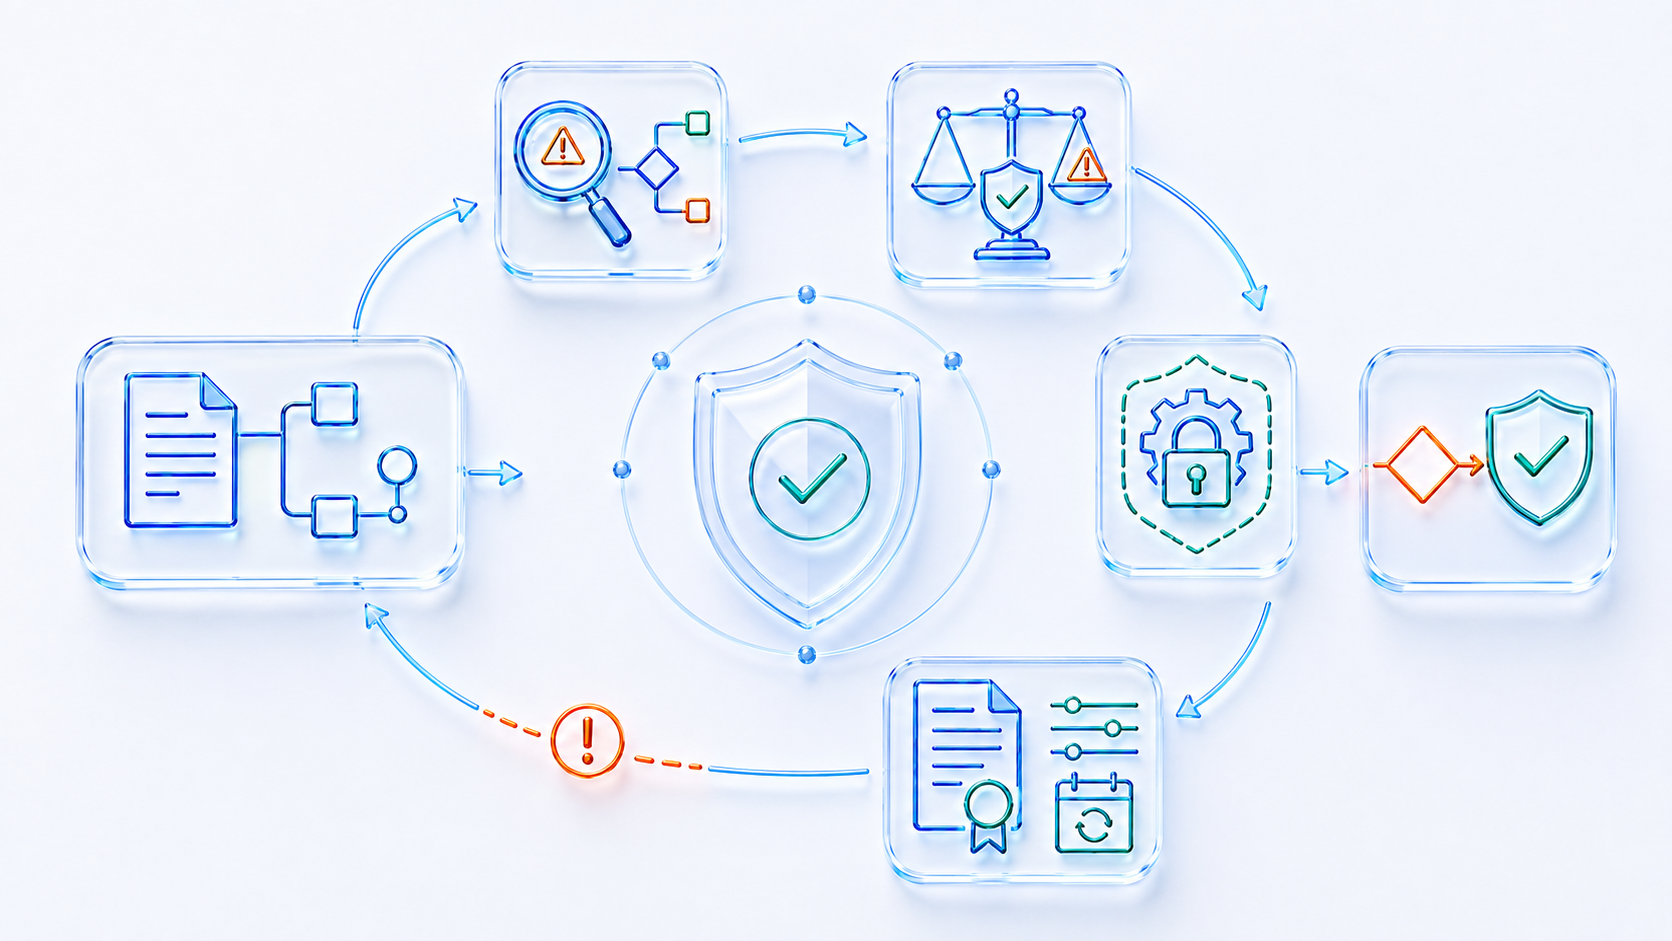
GDPR management software is useful when it turns a policy or legal requirement into a controlled operating route without pretending that the software makes the legal decision. 
 

Requirement

Identify the principle, obligation, policy, contract or risk that makes a control necessary. 


Control

Define the action, decision, safeguard, record or review expected from the responsible role.


Operation

Use questions, logic, assignments and approvals to guide people through the required process. 


Evidence

Retain proportionate evidence of the assessment, action, approval, exception or completed review. 


Assurance

Review whether the control remains current, complete and effective; raise action when it does not. 

ZAP privacy workflow showing DPIA screening risk actions evidence and accountable approval

A REAL CONTROL WORKFLOW

From Proposed Processing to an Accountable Decision

Consider a US service business adding an AI feature to a service offered to EU customers. Record the intended processing, affected individuals, provider, data flows and proposed uses. Screen for the assessments required under the applicable regime, then assign specialist review and resolve safeguards before approving the change. 

  • Describe the nature, scope, context and purpose of the intended processing
  • Screen for indicators that a DPIA may be required
  • Identify affected individuals and potential harm to their rights and freedoms
  • Assess necessity, proportionality, existing controls and residual risk
  • Assign mitigation to named owners with evidence requirements
  • Route the proposal to the appropriate DPO, owner or approving authority
  • Record the outcome, conditions and planned review trigger

A configured route makes missing steps visible. Qualified reviewers decide whether processing may proceed and whether consultation with the relevant supervisory authority is required. 

CONNECTED PRIVACY CONTROLS 

Six Areas Where Workflow Strengthens Accountability

Use these workflows to manage the GDPR duties identified for your organization. Record jurisdiction, responsible entity and applicable requirements so teams can distinguish GDPR processes from other privacy obligations. 


RoPA and data mapping

Assign processing activities to accountable owners, record purposes, categories, recipients, transfers, retention and security measures, then schedule review when activity changes. 


Lawful basis and retention

Record the organization’s selected basis and reasoning, connect applicable policy or assessment evidence and prompt review of retention decisions. 


DPIA and privacy risk

Screen proposed processing, assess risks to individuals, assign mitigation, approve the decision and revisit the assessment when material conditions change. 


Individual-rights requests

Log the request, confirm identity proportionately, assign searches and reviews, monitor the response route and retain the outcome without unnecessarily copying personal data into the workflow.


Processor oversight

Record processors, contract status, services, review dates and due-diligence actions, with links to the relevant processing activity and supplier record. 


Breach assessment and response

Capture the facts, assess risk to individuals, record the notification decision, assign mitigation and retain the response history for subsequent review. 

RIGHTS REQUESTS IN PRACTICE 

Coordinate Access Requests Across Teams and Systems

A subject access request can arrive through different channels and may require contributions from several systems and departments. The risk is not merely a missed diary date; it is an incomplete search, insecure disclosure, inconsistent redaction or a decision without an accountable basis.

  • Record how and when the request was received
  • Confirm identity or authority where reasonably necessary
  • Clarify the requested information only where the conditions allow
  • Assign proportionate searches to relevant data owners
  • Review third-party information, exemptions and response security
  • Approve and issue the response through the agreed route
  • Retain the decision and completion evidence

Configure deadlines and decision points for the applicable law and request type. Record the basis for any clarification, extension or exemption and the responsible reviewer. Do not apply one generic response deadline to every jurisdiction. 

What ZAP controls

  • Ownership and required contributors
  • Configured target dates and notifications
  • Search, review and approval steps
  • Exceptions and unresolved activity
  • Evidence that the response route was completed

What people still decide

  • The scope of a reasonable search
  • Whether an exemption or restriction applies
  • What must be redacted or disclosed
  • How identity and delivery will be handled securely

INCIDENT TO ACCOUNTABLE OUTCOME 

A Breach Workflow Must Support the Decision—Not Make It

Record the incident, awareness time, affected processing and immediate response. Assign qualified reviewers to assess applicable notification duties, recipients and deadlines for each relevant jurisdiction and contract. Track those decisions and actions separately where requirements differ.

01 

Capture

Record the known facts, discovery time, affected processing and immediate containment. 

02 

Classify

Identify data categories, affected people, scale and the nature of the breach. 

03 

Assess

Evaluate likelihood and severity of possible harm to individuals. 

04 

Decide

Authorized reviewers determine which authority, individual or contractual notifications are required and record the rationale. 

05 

Act

Assign mitigation, communication, investigation and corrective action. 

06 

Review

Retain the rationale and revisit controls, risks, training or suppliers affected. 

A timer can prompt urgency. It cannot determine the legal threshold, the risk to individuals or the content of a regulatory notification.

CONTROLLED GOVERNANCE, LIVE ASSURANCE 

Apply the 70/30 Model to Privacy Management

The 70/30 model is an illustrative way to distinguish the controlled framework from live assurance activity, not a measured allocation of effort or a compliance formula. Both need clear ownership and review. 
70% — The controlled framework

Policies, responsibilities, RoPA structure, lawful-basis criteria, retention rules, processor requirements, assessment methods and escalation routes define how privacy should be managed. 

  • Approved policies and procedures
  • Defined control owners and authorities
  • Configured assessment and response routes
  • Review, retention and escalation requirements

30% — The live assurance position

Current requests, assessments, processor reviews, evidence, actions, breaches, overdue work and changed processing activities show whether those controls are operating. 

  • Current records and supporting evidence
  • Open decisions, risks and mitigations
  • Due, overdue and escalated activity
  • Completed reviews and verified outcomes
ZAP privacy assurance dashboard showing control owners reviews evidence and exceptions without personal data

EVIDENCE WITH PROPORTIONATE DATA 

Prove the Control Without Creating Another Privacy Risk

Privacy software should not become an uncontrolled copy of the personal data it is meant to help govern. The workflow should retain enough information to evidence the control while avoiding unnecessary duplication of identity documents, request bundles, investigation material or operational datasets. 

  • Use references or controlled links where the underlying evidence belongs elsewhere
  • Collect only the information necessary for the control decision
  • Restrict access according to role and purpose
  • Apply agreed retention and review arrangements to governance records
  • Separate management reporting from sensitive case detail
  • Confirm how exports and attachments will be handled before configuration

The appropriate boundary depends on the organization’s purpose, systems, risk assessment and data-protection procedure. It should be designed deliberately rather than created by convenience. 

SOFTWARE SUPPORTS ACCOUNTABILITY 

Clear Responsibility Is Part of the Control

ZEBSOFT can provide structured records, permissions, tracked activity, tasks, checklists, notifications, approvals and evidence routes. This is the practical role of GDPR management software. These features support privacy governance; they do not guarantee compliance or replace the controller’s, processor’s, DPO’s or legal advisor’s responsibilities. 


Customer responsibility

The organization decides its purposes, lawful bases, controls, retention, risk tolerance, response decisions and applicable legal obligations. 


Configured system responsibility

The agreed ZAP configuration records and routes the control process, surfaces incomplete activity and retains the permitted evidence. 


ZEBSOFT service responsibility

ZEBSOFT hosts and supports the platform as agreed, with customer data hosted in AWS London and information-security controls supported by ZEBSOFT’s ISO 27001-certified management system. 

The customer remains responsible for confirming that its configuration, procedures, permissions, training and use meet its own privacy obligations.

DEEPER GUIDANCE AND CONNECTED CONTROLS 

Connect Privacy Governance to the Wider Management System

Privacy controls often depend on document control, risk, audit, supplier oversight and information security. Use these pages and primary sources to build the operational context around the GDPR workflow. 


Risk management

Connect privacy risks, mitigation and review activity.

Explore risk management → 


Document control

Control privacy policies, procedures and review activity.

Explore document control → 


Audit management

Assess whether privacy controls are operating and retain findings.

Explore audit management → 


ISO 27001

Link privacy governance to information-security controls.

Explore ISO 27001 software → 

COMMON QUESTIONS 

GDPR Management Software FAQs for US Teams

Does ZEBSOFT control our personal data?

ZAP supports the governance workflow around your source data; it does not automatically control data in other systems. Personal data entered into ZAP records or attachments still requires appropriate access, retention and handling controls. 

Can ZAP guarantee GDPR compliance?

No software can guarantee organizational compliance. ZAP can support accountability by structuring the controls and retaining permitted evidence, but the organization remains responsible for its legal decisions and operating practices. 

Can we manage a RoPA in ZEBSOFT?

ZAP can structure processing activities, owners, purposes, categories, recipients, transfers, retention and security-control descriptions, with workflow for review and change. The organization remains responsible for completeness and accuracy. 

Can ZAP manage SAR and breach workflows?

Configured workflows can allocate tasks, record decision points, prompt target dates and retain response evidence. Authorized people must still assess scope, exemptions, disclosure, breach risk and notification duties. 

Should privacy evidence be uploaded into ZAP?

Only where necessary and permitted by the organization’s procedure. A reference or controlled link may be more appropriate when the underlying evidence contains personal or sensitive information. 

Can the privacy controls connect to other modules?

Yes. Privacy risks, policies, audits, training, incidents, suppliers and corrective actions can be related within the wider ZEBSOFT platform, subject to the agreed configuration and permissions.

ZAP IT. KNOW IT. FIX IT.

Make Privacy Controls Visible, Accountable and Reviewable

Bring one privacy workflow from your US operations, such as an EU customer request, DPIA, processing-register review or vendor assessment. Discuss scope, evidence and approvals with our UK-based team, including data-location requirements and time-zone coordination.