ISO 27001 CONTROL GOVERNANCE. HUMAN ACCOUNTABILITY. 

Statement of Applicability Software for US Teams

ISO 27001 Control Decisions, Connected Evidence and Human Accountability

Zebsoft helps US security and compliance teams maintain a controlled Statement of Applicability for their ISO/IEC 27001 information security management system. Connect control decisions, justifications, implementation status, owners and evidence across US facilities, remote teams and service providers. Keep customer security commitments and risk treatment connected to the people responsible for delivery.

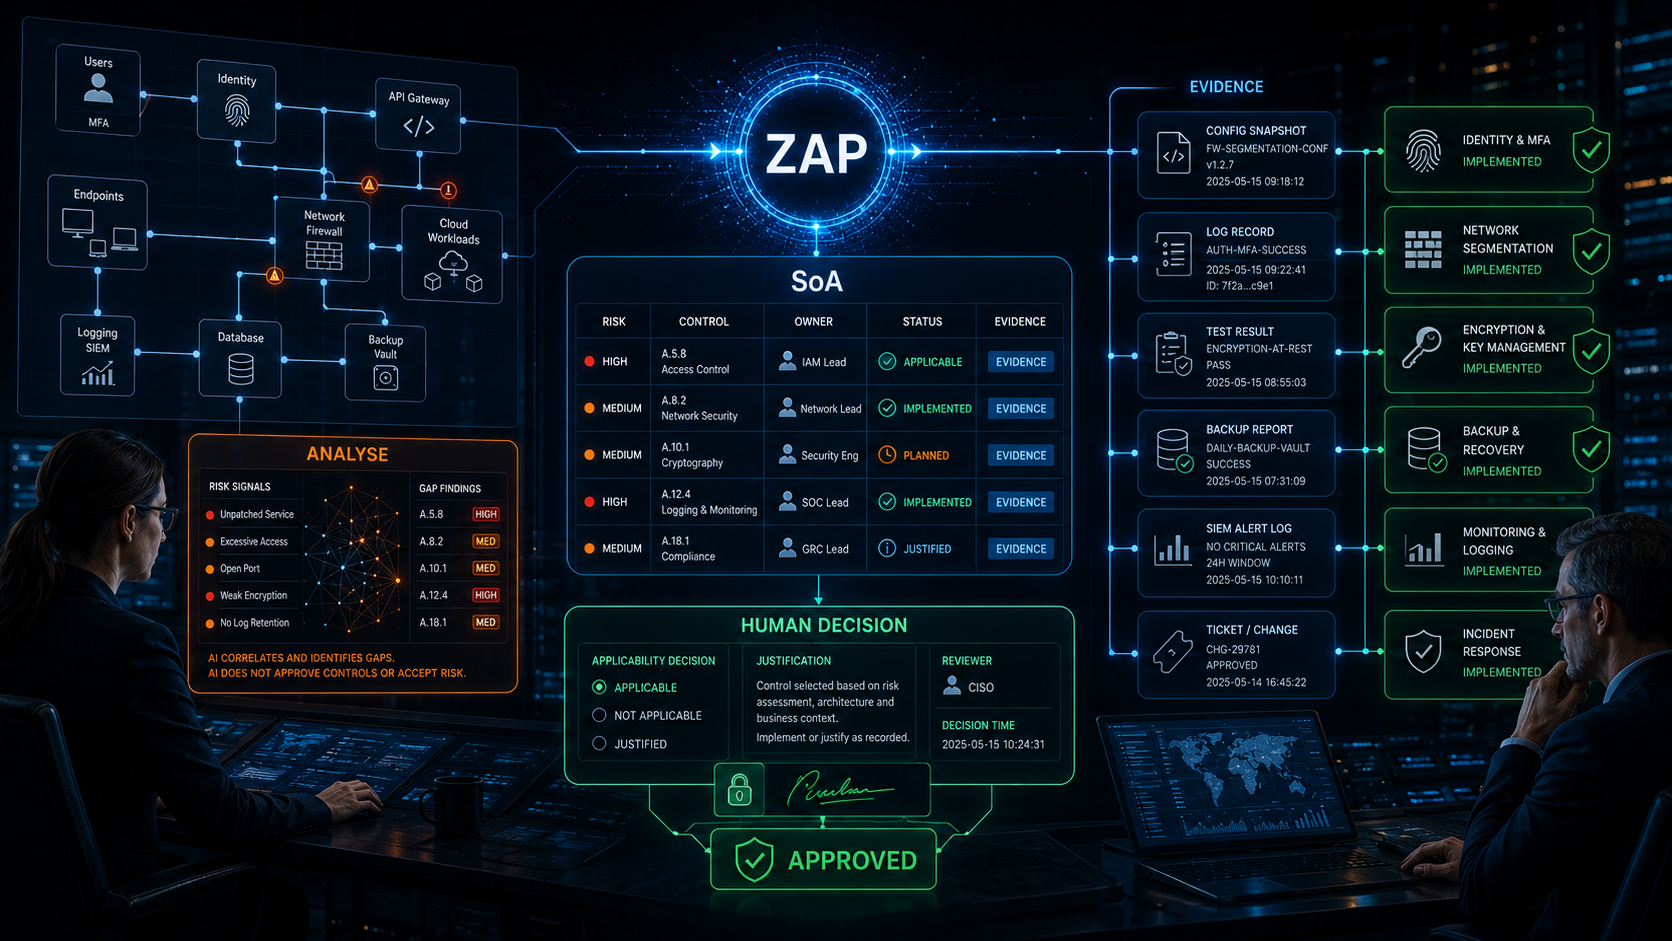
ZAP AI may examine approved information, analyze relationships and identify matters for review. AI output can be incomplete or incorrect and must be checked against its sources. Authorized people determine control needs, verify evidence, approve the SoA and accept risk. 
  • Maintain a controlled SoA register rather than an isolated spreadsheet
  • Link each control decision to risk treatment and supporting context
  • Separate claimed implementation from evidence of operation and effectiveness
  • Record human review, challenge, approval and change history
ISO 27001 Statement of Applicability governance with human approval and connected evidence

WHAT THE SoA ACTUALLY GOVERNS 

A Controlled Record of Security Decisions

The Statement of Applicability is not a catalog of software features and it is not a declaration that every Annex A control must be adopted. It records which controls the organization has determined are necessary, why controls are included, whether they are implemented and why any Annex A controls are excluded. 


Decision context

For a US organization, the SoA should reflect the ISMS scope, information-security risks, risk treatment and applicable federal, state, sector, contractual and customer requirements. Record which obligations apply to which services, locations and data flows; do not assume one control position covers every operation. 


Control position

Each entry needs an intelligible applicability position and rationale. A status without context does not explain the organization’s reasoning or accountability. 


Current governance

Ownership, implementation, evidence, approval and review should remain controlled as systems, threats, suppliers, obligations and business activities change.

Zebsoft structures and connects the record. The organization decides what is necessary and remains accountable for that decision. 

RISK TREATMENT BEFORE CHECKLISTING 

Annex A Is a Reference Set, Not a Substitute for Judgment

The organization determines the controls needed to treat its information-security risks. Annex A is then used as a reference to check that necessary controls have not been omitted. Controls may also arise from legislation, regulation, contracts, customer requirements, sector rules, technology architecture or the organization’s own design.

A copied control list with generic justifications may look complete while concealing weak reasoning. The better question is not “Have we ticked every box?” but “Can we explain why this control is or is not necessary in our context?” 

What a credible SoA should reveal

  • The ISMS scope and risk context behind the decision
  • Controls selected through risk treatment, including controls outside Annex A where necessary
  • A reasoned inclusion or exclusion position
  • Whether the control is implemented—not merely planned or discussed
  • The people authorized to own, review and approve the position
  • Evidence that can be examined without overstating effectiveness

THE GOVERNED SoA LIFECYCLE

From Scope and Risk to Review and Approval

Zebsoft can organize the work around the SoA while keeping decision authority with competent people. 

01 

Define scope

Authorized management establishes the boundaries, interfaces, activities, locations, technology and exclusions relevant to the ISMS. 

02 

Assess risk

People identify information-security risks, evaluate them using the approved method and determine treatment priorities. 

03 

Determine controls

Control needs are selected from risk treatment, obligations and operational context—not generated from a generic prompt. 

04 

Decide applicability

Competent owners decide inclusion or exclusion and record the reasoning for the organization’s position. 

05 

Plan implementation

Accountable owners define what will be implemented, by whom, where, when and with what acceptance criteria. 

06 

Link evidence

Policies, configurations, training, supplier records, tickets, tests and other evidence are connected to the relevant control. 

07 

Review and approve

Authorized people challenge the rationale, resolve gaps, accept residual risk and approve the controlled SoA. 

08 

Monitor change

Risk, incidents, audits, technology and obligations trigger review so the SoA does not become a dated snapshot.

ONE CONNECTED CONTROL REGISTER 

What Zebsoft Statement of Applicability Software Controls

The platform provides structure, routing and traceability around each control record. Configuration should reflect the organization’s own ISMS design and authority model. 


Control identity

Maintain the control reference, title, theme, source and any organization-specific control without losing its provenance. 


Applicability rationale

Record inclusion or exclusion reasoning in a required field rather than leaving an unexplained status in a spreadsheet. 


Implementation status

Distinguish planned, partly implemented, implemented and review states using the organization’s approved definitions. 


Named ownership

Allocate responsibility for maintaining the control and its evidence while preserving management accountability. 


Risk relationships

Connect controls to identified risks, treatment actions and residual-risk decisions so the reasoning can be followed. 


Evidence links

Associate approved documents, records, audits, training, tests, incidents and actions without treating an attachment as proof by itself. 


Review scheduling

Set review dates, notifications and escalation paths appropriate to risk, change and the organization’s governance rules. 


Controlled history

Retain changes to status, rationale, ownership, evidence and approval so reviewers can understand how the position evolved. 

RESPONSIBLE AI WITHIN THE ISMS 

Interrogate, Analyze and Challenge—Never Invent Responsibility

ZAP AI is used as an analytical assistant over information the organization has authorized it to examine. It can help a reviewer navigate a large SoA, compare related records and bring possible inconsistencies to attention. Its output is a prompt for human investigation, not an organizational decision.

We deliberately reject the idea that an AI should generate a polished but unsupported SoA. A plausible paragraph is not evidence. A suggested justification is not risk acceptance. A statistical answer is not management approval. 

  • Identify controls with missing, duplicated or unusually generic rationale
  • Flag conflicts between applicability, implementation status and linked evidence
  • Surface stale evidence, overdue reviews, unassigned ownership or unresolved actions
  • Compare control records with risks, incidents, audits, policies and training records
  • Summarize authorized evidence for a reviewer while retaining links to the source
  • Record whether a human accepted, rejected or investigated an AI-raised observation

AI does not approve the SoA. Scope, applicability, exclusion justifications, residual-risk acceptance and implementation claims require authorized human decisions. Reviewers must check AI output against genuine records before using it. 
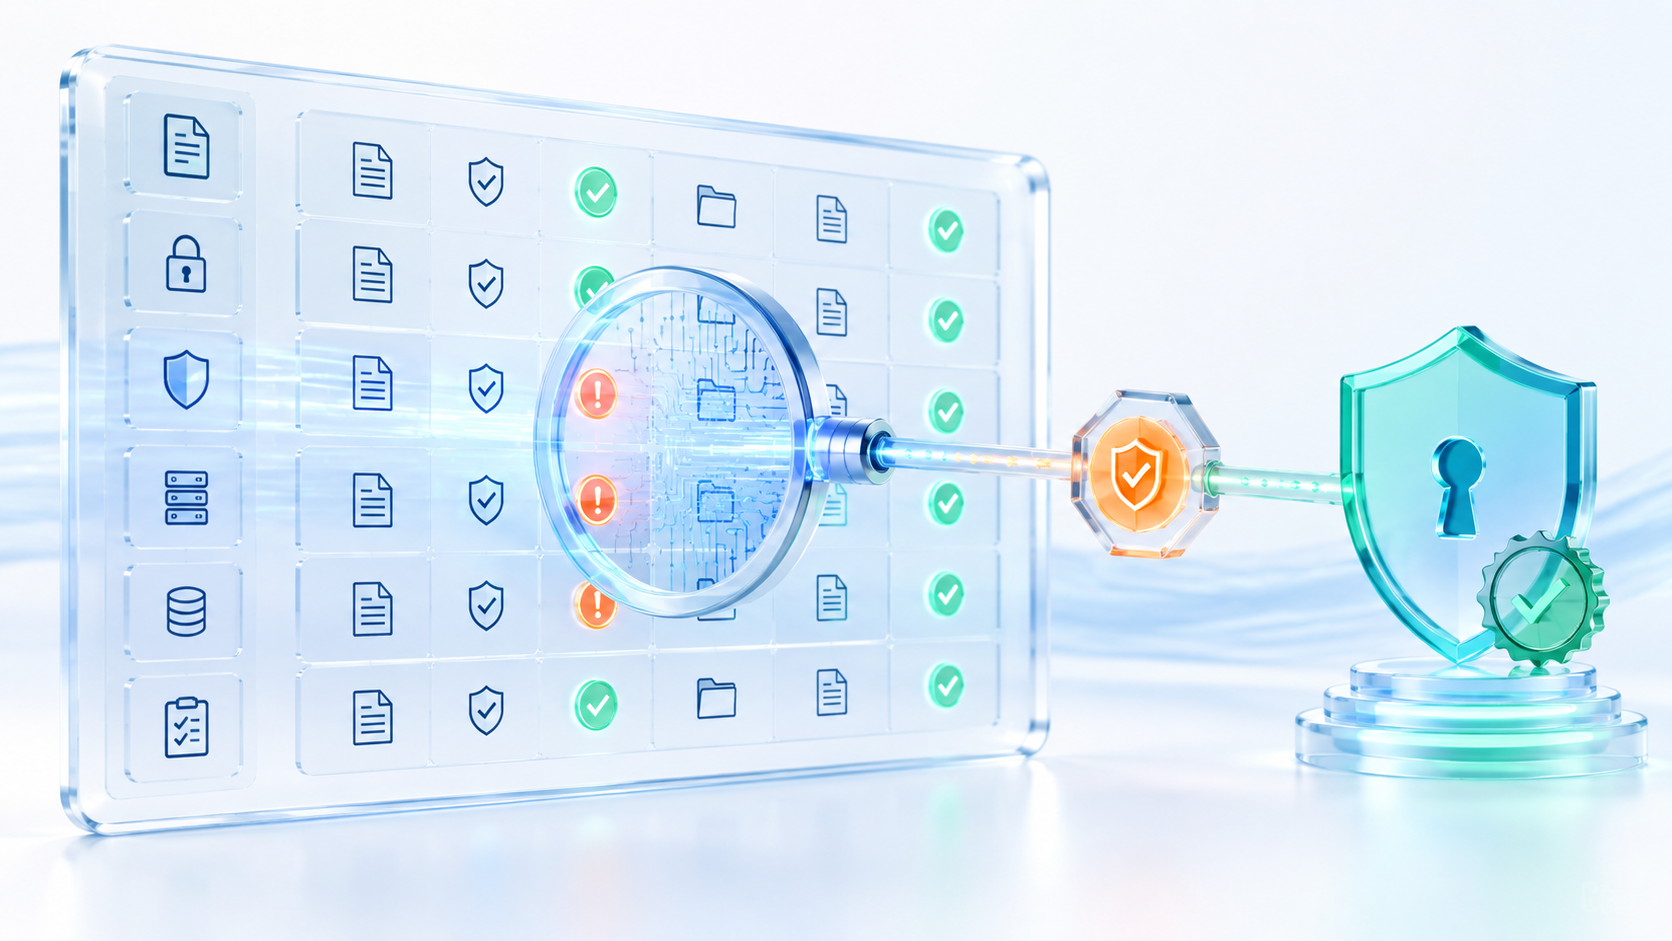
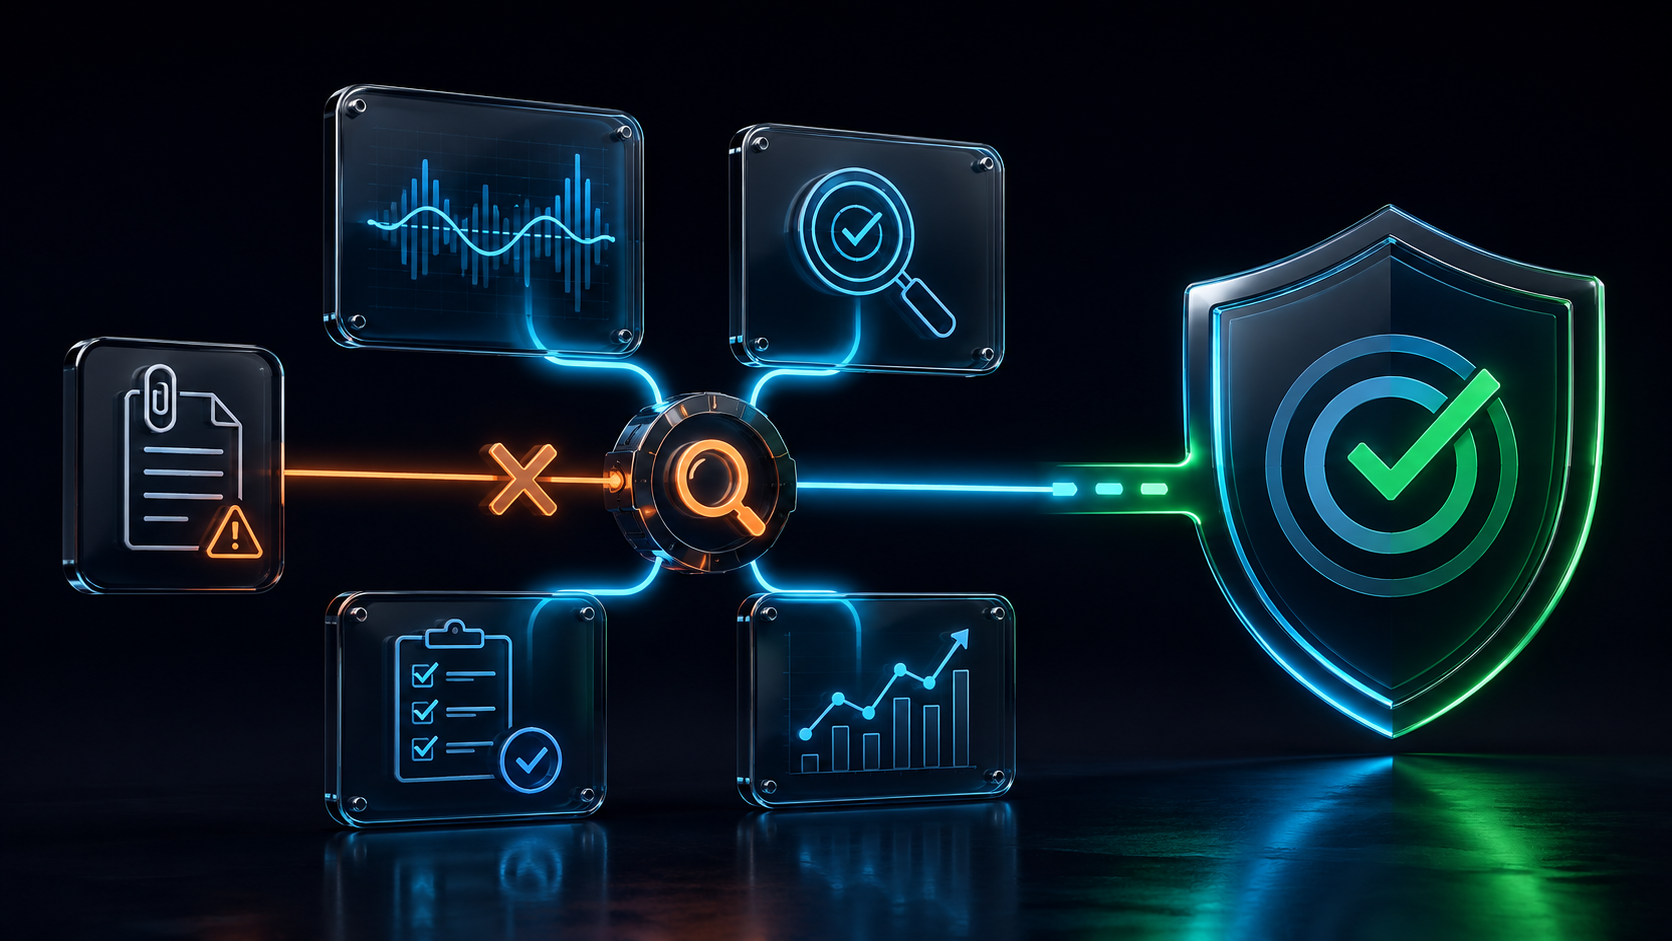
ZAP AI analyses SoA evidence and routes observations to accountable human reviewers

DECISIONS BELONG TO PEOPLE 

Human Accountability Is Designed Into the Workflow

Responsibility cannot be delegated to an algorithm. Zebsoft can route decisions to the right role and retain the record of review, but the organization defines who is competent and authorized. 


Top management

Sets direction, provides resources, reviews performance and remains accountable for the effectiveness of the ISMS. 


ISMS manager

Coordinates the SoA, protects its integrity and ensures decisions are routed through the agreed governance process. 


Risk owner

Evaluates treatment choices and makes or escalates residual-risk acceptance within delegated authority. 


Control owner

Maintains implementation, operational evidence, review activity and actions for the assigned control. 


Internal auditor

Independently examines conformity and effectiveness; the auditor should not own the controls being audited. 

An AI-generated recommendation may inform these people. It never replaces their competence, authority, professional judgment or recorded decision. 

ISO/IEC 27001:2022 ANNEX A 

Organize the Reference Controls Without Losing Risk Context

The 2022 control set is organized into four themes. Zebsoft can present those controls alongside organization-specific and externally required controls, while the organization determines what is necessary. 


Organizational controls

Governance, policies, responsibilities, suppliers, incidents, continuity, legal obligations and related organizational arrangements. 


People controls

Screening, terms of employment, awareness, disciplinary processes, remote working and reporting responsibilities. 


Physical controls

Perimeters, entry, facilities, monitoring, equipment, media, clear desk and protection from physical or environmental threats. 


Technological controls

Identity, access, authentication, malware, vulnerability, logging, network, development, configuration and other technical safeguards. 

ISO/IEC 27002 provides implementation guidance for information-security controls. It does not replace the organization’s own risk treatment, design choices or accountability. 
Live ISO 27001 SoA register with control ownership risk links evidence and review status

FROM ASSERTION TO EXAMINABLE EVIDENCE 

An Attachment Is Not Automatically Proof of Control Effectiveness

A policy can show that a control was designed. A configuration record may show that it exists. Logs, samples, tests, interviews, incident outcomes and audit results may provide evidence about whether it operates and achieves the intended result. Those are different assurance questions.

Zebsoft can connect each control to several evidence types and retain review history. The reviewer decides whether the evidence is authentic, relevant, sufficient, current and within scope. 

  • Design: what the approved control is intended to do
  • Implementation: whether the control has been put in place
  • Operation: whether the control is being performed as defined
  • Effectiveness: whether the control contributes to the intended risk treatment
  • Exception: what gaps, incidents, findings or accepted limitations remain

KEEP THE SoA CURRENT 

Review When the Organization or Its Risk Changes

A review date helps, but material change should also prompt attention. ZAP can monitor connected records and raise a review task without silently rewriting the approved SoA. 


Technology and architecture

New systems, cloud services, integrations, remote-working arrangements, data flows or material configuration changes may affect existing controls. 


Threats and events

Incidents, vulnerabilities, threat intelligence, audit findings and control failures may challenge assumptions or show treatment is inadequate. 


Business and obligations

Scope, sites, services, suppliers, contracts, laws, customer requirements, acquisitions and organizational roles may change applicability. 

New or changed AI use is also a review trigger

When the organization adopts AI services, it should assess information assets, data flows, suppliers, access, privacy, accuracy, security, retention and human-oversight risks. The ISMS can govern those risks; ISO/IEC 42001 may provide a complementary management-system framework for responsible AI use. The two standards should not be presented as interchangeable. 

A REAL-WORLD REVIEW ROUTE 

When a US Customer Review Exposes a Control Gap

A US service provider is preparing a customer security response. Its access-control record is marked implemented, but an acquisition has introduced another identity system. An AI observation starts a review; a competent owner verifies the facts. 

01 

Observation

ZAP flags an access-control record with old evidence and a changed owner. The reviewer checks whether the acquired business is covered by the recorded control. 

02 

Human triage

The ISMS manager checks scope, customer commitments and the two identity systems before deciding what requires investigation. 

03 

Owner response

The authorized owner supplies access-review evidence for each in-scope system, records any gap and assigns a corrective action with a due date. 

04 

Approval

The designated authority reviews the risk, approves the revised control position and decides what can accurately be stated in the customer response. 

The result is a traceable chain from machine-raised observation to human examination, evidence and authorized decision. 

MANAGEMENT AND AUDIT VIEW 

Report the Position Without Hiding Its Limitations

Dashboards and exports can help management and auditors navigate the SoA, but presentation should not turn uncertainty into a green badge. A useful view distinguishes complete records from overdue reviews, unsupported claims, open actions and unresolved exceptions. 

  • Applicability and exclusion decisions awaiting approval
  • Controls without current owners or review dates
  • Implementation status by theme, US facility, service or accountable role
  • Controls with weak, expired or missing evidence
  • Open risks, audit findings, incidents and treatment actions
  • Full change and approval history for the controlled SoA

The organization defines reporting criteria and decides what the indicators mean. Zebsoft displays recorded information; it does not certify that the organization conforms. 
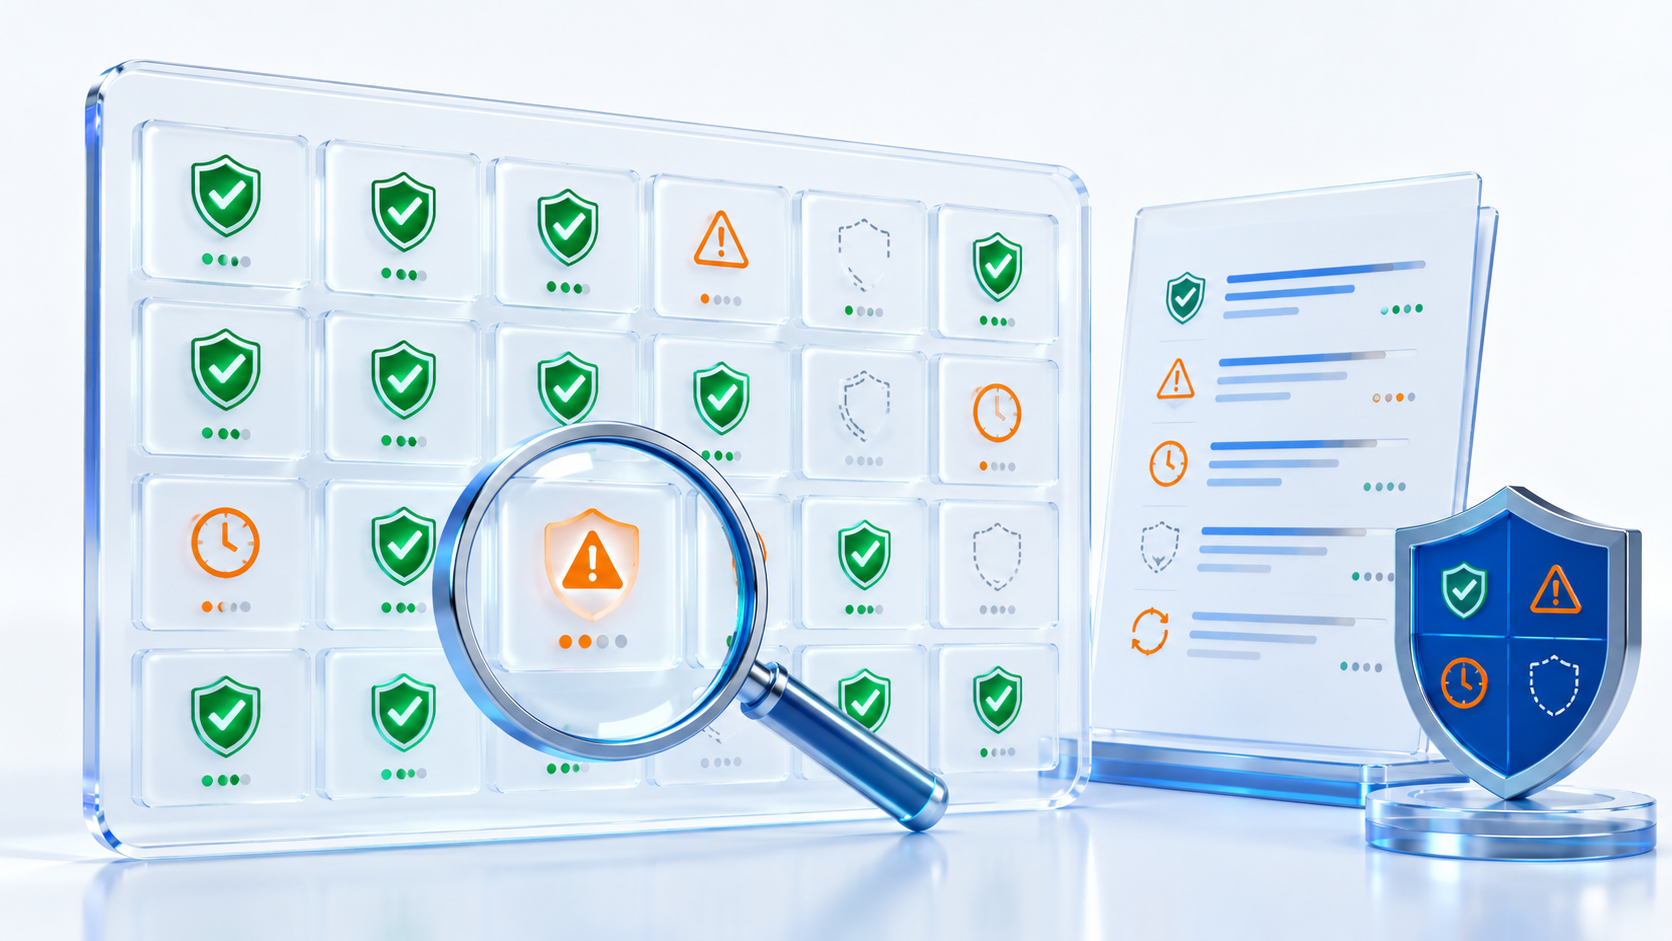
ISO 27001 SoA dashboard with implementation evidence gaps overdue reviews and approvals

CONNECTED ISMS GOVERNANCE 

The SoA Makes More Sense When Its Sources Remain Connected

A static export may satisfy a document request, but the working governance value comes from links to the records that explain and test the control position. 


Risk management

Connect control selection and treatment decisions to the live risk context. Explore risk management software. 


Document control

Link approved policies, standards, procedures and technical information without confusing documents with operating evidence. Explore document control. 


Audit and assurance

Use audits to examine whether controls operate as intended and route findings into accountable action. Explore the auditing platform. 


People and training

Connect role, competence, awareness, acknowledgments and assigned responsibility to the controls that depend on people. 

CLEAR PRODUCT BOUNDARIES 

What Zebsoft Supports—and What the Organization Must Supply

Zebsoft can support

  • A structured control register with configured fields and statuses
  • Workflow for review, challenge, approval, actions and reminders
  • Links between controls, risks, evidence, documents, audits and people
  • Traceable history and reporting over authorized records
  • AI-assisted interrogation and analysis with source-linked human review

The organization remains responsible for

  • Defining ISMS scope, context, risk criteria and method
  • Identifying risks and determining necessary controls
  • Making and justifying applicability or exclusion decisions
  • Implementing controls and supplying authentic evidence
  • Evaluating effectiveness, accepting risk and approving the SoA
  • Meeting applicable legal, contractual, regulatory and certification requirements

INFORMED IMPLEMENTATION 

Standards References and Practical Questions

Use the licensed standards and competent advice applicable to your organization. Product content is informative and is not certification, legal advice or a substitute for the standard. 


ISO/IEC 27001:2022

Specifies requirements for establishing, implementing, maintaining and continually improving an ISMS. View the official ISO standard page. 


ISO/IEC 27002:2022

Provides guidance and good practice for information-security controls used within an ISMS. View the official ISO standard page. 


ISO/IEC 42001:2023

Provides a management-system framework for responsible development, provision or use of AI systems. View the official ISO standard page. 

Can AI write our Statement of Applicability?

It can assist analysis and drafting for human review, but Zebsoft’s approach is not to manufacture an approved SoA. Scope, risk treatment, applicability, exclusions, evidence, risk acceptance and approval require authorized human judgment. 

Does every Annex A control have to be implemented?

No blanket answer should be generated. The organization determines necessary controls through risk treatment and other requirements, uses Annex A as a reference and justifies exclusions in its SoA. 

Does linked evidence prove effectiveness?

No. It makes evidence accessible and traceable. Competent reviewers and auditors still evaluate authenticity, relevance, sufficiency, currency, operation and effectiveness. 

Can Zebsoft guarantee certification?

No. Zebsoft provides governance capability. Certification depends on the organization’s ISMS, implementation, evidence and independent assessment against applicable requirements. 

SEE THE GOVERNED SoA WORKFLOW 

Bring a Real Control Decision—Not a Generic Checklist

Bring a real US customer requirement, an access-control review or a control shared across several facilities. We can demonstrate how ZAP connects risk, ownership, evidence and approval. ZEBSOFT is UK-based; discuss US time-zone coverage, AWS London hosting and rollout requirements during scoping.