CONNECTED AUDIT ASSURANCE

Audit Management Software for Operational Assurance

Plan, Perform, Follow Through and Verify the Result

Zebsoft audit management software connects audit programmes, scope, criteria, fieldwork, evidence, findings, actions and verification within one governed assurance system.

Use the same platform for ISO internal audits, supplier audits, operational inspections, multi-site programmes and risk-based assurance activity—without allowing the audit trail to end when the report is issued.
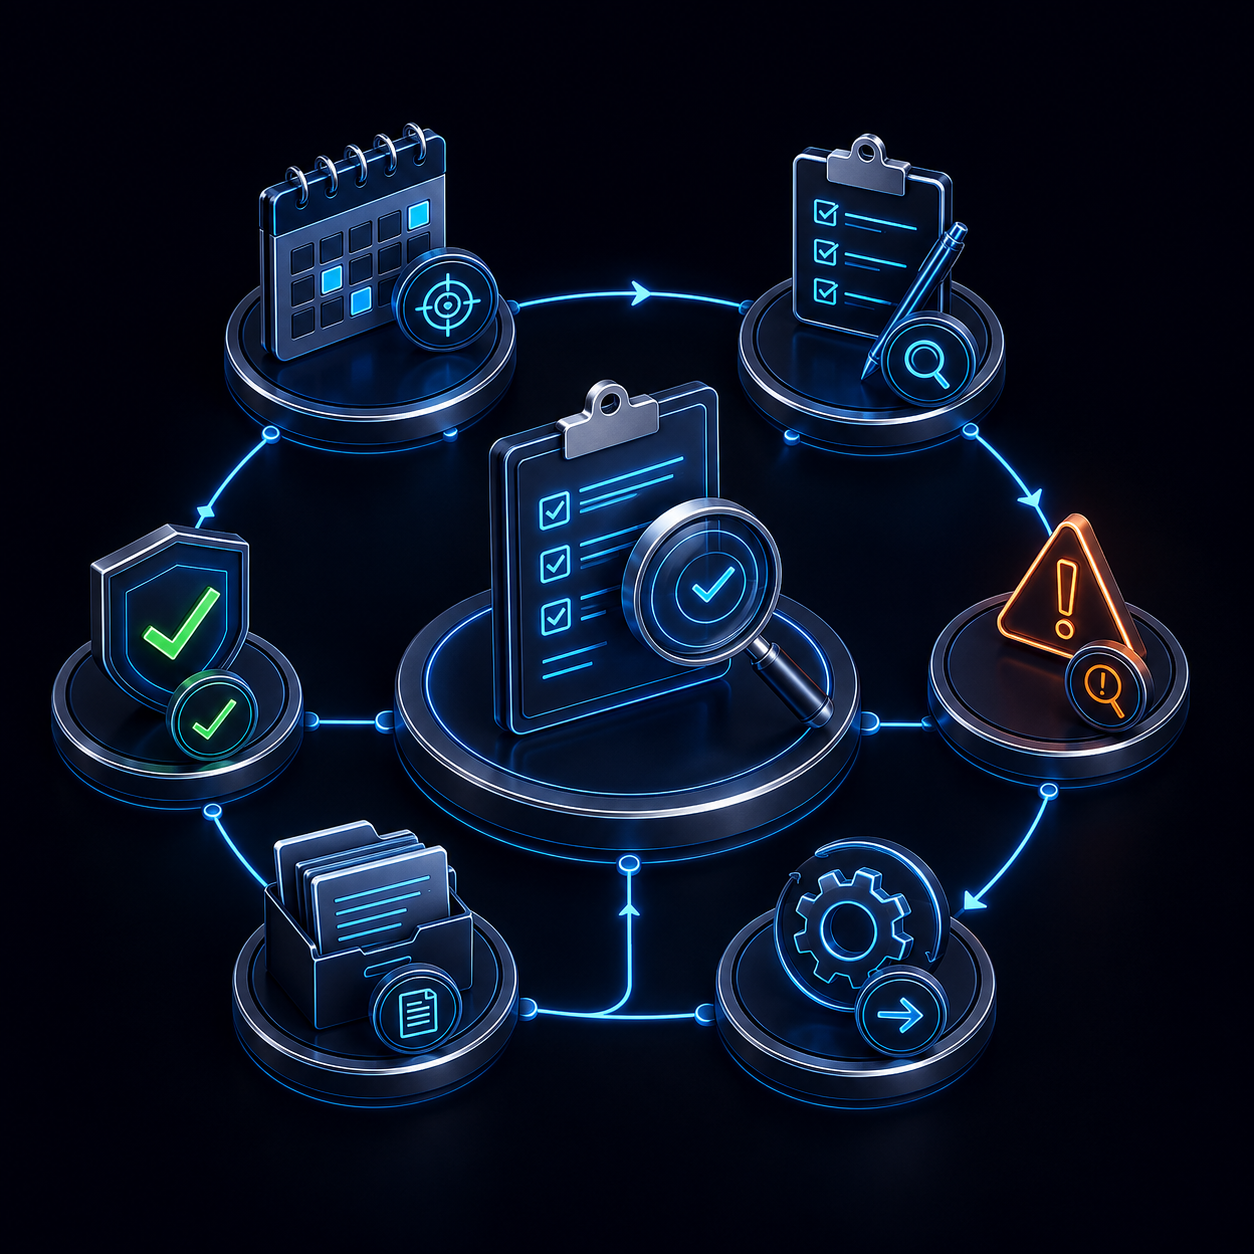
  • Risk-informed audit programmes and schedules
  • Controlled fieldwork, evidence and findings
  • Actions, escalation and effectiveness verification
Audit management software for connected operational assurance

THE OPERATIONAL GAP

Audits Should Not End in Reports

An audit report records what the auditor concluded at a point in time. It does not, by itself, ensure that the underlying risk was reassessed, the corrective action was appropriate, the procedure changed, affected people were informed or the response was later shown to work.

Where audit planning sits in one application and remediation is managed through email, spreadsheets or another system, the organisation must reconstruct the relationship afterwards. Status may look complete while operational weakness remains unresolved.

The loss of connection usually appears as

  • Findings copied manually into separate CAPA or action registers
  • Evidence stored without a clear relationship to scope, criteria or test
  • Owners receiving actions without the decision context behind them
  • Closure based on task completion rather than effectiveness
  • Training, documents and risks updated through unrelated processes
  • Management reports assembled after the event from conflicting sources

THE COMMERCIAL DIFFERENCE

More Than an Audit Repository or Inspection App

Modern audit products are expected to support planning, fieldwork, evidence, findings, remediation and dashboards. Zebsoft meets that operational expectation, then extends the connection into the wider management system where the response must be implemented and assured.

Spreadsheets and folders

Flexible for small lists, but programmes, evidence, versions, ownership and follow-up depend on manual discipline. Current assurance is difficult to establish across sites.

Generic inspection apps

Useful for repeatable checks and rapid evidence capture. Wider governance, audit independence, risk linkage and controlled remediation may require additional systems.

Dedicated audit stacks

Can provide sophisticated audit-team methods and reporting. Operational owners may still complete risks, documents, training and changes in adjacent applications.

Zebsoft assurance

Audit operates alongside the risks, controls, information, people and actions it is testing, preserving context from programme decision to verified outcome.

DEFINE—COMMUNICATE—OPERATE—ASSURE

Build Auditing Into the Operating System

The audit function is most valuable when it tests a defined expectation, communicates activity clearly, observes real operation and returns an evidence-based assurance decision.

Define

Establish the audit universe, objectives, risk context, programme, scope, criteria, methods, competence, evidence expectations and authority route.

Communicate

Notify the relevant auditors and auditees, request information, clarify responsibility and keep changes to timing or scope visible.

Operate

Perform fieldwork, testing, interviews, sampling and review; record evidence and findings; and initiate the approved response workflow.

Assure

Review conclusions, monitor actions, examine effectiveness and retain the verified outcome, exception or residual concern for oversight.

THIS IS HOW WE SOLVE THE PROBLEM

One Controlled Audit Lifecycle

Configure the stages and authority appropriate to the organisation. The lifecycle below shows how Zebsoft keeps the decision, work, evidence and follow-through connected.

01

Prioritise

Use the audit universe, risk, previous results, obligations and management priorities to decide where assurance effort is needed.

02

Plan

Set the programme, audit owner, team, timing, location, objective, scope, criteria and expected route for evidence and reporting.

03

Prepare

Communicate the audit, review relevant information, configure the checklist or work programme and request preliminary evidence.

04

Perform

Complete interviews, observation, sampling, testing and record review while preserving evidence, notes and professional judgement.

05

Conclude

Record conformity, observation, opportunity, weakness or nonconformity and retain the criteria, evidence and rationale supporting the conclusion.

06

Respond

Assign correction, investigation, corrective action, risk review or change through the configured workflow with accountable ownership.

07

Verify

Confirm whether the response was implemented and effective, or retain the exception, escalation and further assurance requirement.

RISK-BASED PROGRAMME MANAGEMENT

Direct Audit Effort Where Assurance Matters Most

A fixed annual calendar may remain appropriate for mandatory or recurring activity, but the programme should also respond to changing risk, incidents, supplier performance, overdue actions, process change and previous audit results.

Zebsoft can keep those signals visible alongside planned activity so competent audit leadership can adjust coverage rather than simply repeat last year’s schedule.
  • Central audit universe and programme visibility
  • Recurring, event-driven and one-off audit activity
  • Scope by site, process, supplier, asset, standard or control
  • Auditor and lead-auditor assignment
  • Current status, overdue work and programme exceptions
  • Management reporting across programmes and locations

Risk informs the plan—people approve it

System information can support prioritisation and highlight changing exposure. Audit leaders remain responsible for professional judgement, independence, competence, scope, resource allocation and programme approval.

The software should make those decisions visible and traceable; it should not conceal them behind an automatic score.

Audit fieldwork evidence findings and assurance workflow

CONTROLLED FIELDWORK AND EVIDENCE

Keep Evidence Attached to the Question It Answers

An attachment is not automatically audit evidence. Its value depends on source, relevance, period, integrity and the test or conclusion it supports. Zebsoft keeps evidence within the audit context rather than treating the final report as the only important record.

Auditors can work through configured questions and test steps, retain notes and supporting information, and record the conclusion appropriate to the approved method. The organisation decides the evidence rules, access, retention and sign-off requirements.

  • Structured digital audit forms and reusable checklists
  • Questions, criteria, guidance and expected evidence
  • Documents, images, notes and supporting records
  • Scoring or logic where the approved method requires it
  • Finding classification, severity and rationale
  • Traceable review, sign-off and retained history

FROM FINDING TO VERIFIED RESPONSE

Closure Is a Decision—not a Ticked Task

A due date and completed action are useful, but neither proves that the underlying issue was understood or that the response worked. Zebsoft keeps the audit conclusion connected to the operational response and its later verification.

Finding and context

Retain the audit, criterion, test, evidence, affected process or location, classification and auditor’s rationale behind the finding.

Correction and containment

Record immediate action required to control the current problem without confusing short-term correction with systemic corrective action.

Investigation and cause

Route analysis to competent owners, retain relevant information and distinguish evidence-supported cause from assumption or convenient explanation.

Controlled action

Assign approved action, authority, due date and required evidence. Keep missed response, rejection and escalation visible.

Effectiveness review

Define what will demonstrate that the response achieved its intended result and schedule a suitable human verification point.

Assurance outcome

Accept closure, request further work, revise the risk position or retain an exception with the decision and supporting evidence intact.

AUDIT TYPES AND ASSURANCE USES

One Audit Capability—Configured for Different Contexts

Audit terminology, independence, competence, criteria and reporting differ by purpose. Zebsoft provides shared capability that can be configured around the approved method rather than forcing every activity through one generic template.

ISO internal audits

Plan and perform management-system audits against defined criteria while retaining objective evidence, findings and follow-up.

Supplier audits

Assess external-party capability, controls, evidence and agreed requirements and connect findings to approval and continued monitoring.

Operational inspections

Run repeatable site, process, equipment or service checks with evidence, exceptions and prompt action routes.

Compliance evaluations

Examine fulfilment of selected legal, regulatory, contractual or internal obligations using an approved evaluation method.

Information-security audits

Test controls, implementation and supporting evidence across the approved information-security audit scope.

Health-and-safety audits

Evaluate arrangements, operational controls, records and workplace evidence without reducing safety assurance to checklist completion.

Environmental audits

Assess aspects, obligations, controls, monitoring and operational evidence within the organisation’s environmental system.

Multi-site programmes

Apply common methodology and local scope while maintaining programme visibility, comparison and controlled site-level responsibility.

PROGRAMME VISIBILITY AT SCALE

See the Programme Without Flattening Local Context

Central audit teams need a coherent view across locations, functions, standards and suppliers. Local owners need to see the audits, evidence requests, findings and actions for which they are responsible.

Zebsoft can present both views through shared data and permissions. Central reporting does not require every site to lose its operational context, and local activity does not have to disappear into separate spreadsheets.

Programme controls

  • Planned, active, completed and overdue audit status
  • Programmes by standard, domain, site, supplier or business unit
  • Common templates with controlled contextual variation
  • Lead auditor, team, auditee and action-owner visibility
  • Open findings, ageing, escalation and effectiveness status
  • Evidence-based reporting for management review and oversight

CONNECTED CAPABILITIES

The Audit Trail Continues Into the Management System

The connection is governed by permissions and configuration. It allows an audit conclusion to initiate the relevant operational response without copying information into another uncontrolled register.

Risk and controls

Use audit results to inform risk review, control assurance and treatment decisions while preserving the distinction between audit evidence and management ownership.

Document control

Initiate review or revision where an audit identifies obsolete, unclear or ineffective controlled information and retain the approval route.

Training and competence

Connect competence gaps to role requirements, learning, evidence and authorised review rather than closing them with an attendance record alone.

Incident management

Relate audit findings to relevant incidents, complaints or nonconformities where shared cause, control weakness or trend requires investigation.

Change management

Route material changes through impact assessment, approval, implementation, communication and verification before treating the response as complete.

Supplier assurance

Carry supplier-audit results into approval, conditions, development, escalation and continued monitoring with the evidence relationship intact.

MOVE FROM LEGACY AUDIT ADMINISTRATION

Transition Without Losing the Audit History You Still Need

Moving from spreadsheets, SharePoint lists or another audit platform should be treated as a controlled information transition. The aim is not to import every obsolete field; it is to preserve the records, relationships and current commitments needed for operation and assurance.

01

Inventory

Identify programmes, templates, audits, findings, actions, evidence, users and reporting history across the current sources.

02

Decide

Agree what must migrate, what should remain archived, what requires cleansing and which open commitments must remain live.

03

Configure

Build the target audit types, classifications, workflows, permissions, evidence rules, notifications and reporting views.

04

Validate

Test representative records and workflows with suitable users before wider release, then reconcile the agreed transition scope.

RESPONSIBLE AI IN AUDITING

Use AI to Interrogate Approved Information—not Replace Audit Judgement

Where enabled and authorised, AI can assist users in interrogating approved audit information, identifying patterns, summarising recorded activity and supporting analysis. Its output must remain traceable to suitable source information and subject to human review.

AI does not determine audit scope, invent evidence, make a finding, assign root cause, accept a management response or decide that corrective action was effective. Those decisions remain with competent and authorised people.

The retained human decisions

  • Audit programme and engagement approval
  • Competence, independence and team assignment
  • Scope, criteria, method and sampling judgement
  • Evidence sufficiency and finding classification
  • Cause, action and risk acceptance
  • Closure and effectiveness verification

PRACTICAL QUESTIONS

Audit Management Software FAQs

Audit methods, independence requirements, evidence rules and reporting responsibilities vary by organisation and purpose. Zebsoft should be configured around the arrangements your competent people have approved.

What is audit management software?

Audit management software controls the lifecycle around audit planning, scope, fieldwork, evidence, findings, reporting, response and follow-up. Zebsoft also connects the audit outcome to relevant operational workflows and retained assurance evidence.

Can Zebsoft support ISO internal audits?

Yes. Audit programmes, criteria, checklists, evidence, findings and follow-up can be configured to support internal management-system audits. The organisation remains responsible for competence, independence, methodology and conformity decisions.

Can we run supplier and operational audits?

Yes. Shared audit capability can be configured for supplier assessments, site inspections, process audits and other assurance activity with different scope, questions, classifications, permissions and reporting routes.

Does Zebsoft support risk-based audit planning?

Risk information, previous findings, incidents, changes and performance can inform programme decisions. Audit leadership remains responsible for prioritisation, coverage, resource allocation and approval of the audit plan.

Can findings create corrective actions?

Yes. Findings can initiate correction, investigation, CAPA, change or other configured action workflows with ownership, due dates, evidence, escalation and later effectiveness review.

Can evidence be attached to audit records?

Yes. Supporting documents, images, notes and other authorised records can be retained in the relevant audit context. The organisation defines suitability, access, retention and evidential requirements.

Can we migrate from spreadsheets or another audit system?

Yes, subject to source access and quality. Programmes, templates, selected history, open findings and current actions can be assessed and mapped through a phased transition and validation process.

Does the software guarantee audit or certification success?

No. Software cannot guarantee a favourable audit, certification or compliance outcome. Zebsoft supports controlled activity and evidence; competent people remain responsible for audit conclusions, management decisions and effective operation.

SEE ONE REAL AUDIT WORKFLOW

Follow the Finding Beyond the Report

Bring one representative audit route to a demonstration—such as a multi-site internal audit, supplier assessment or recurring operational inspection. We can show how scope, fieldwork, evidence, finding, response and effectiveness remain connected.

Start with the audit problem

The most useful demonstration begins with your programme structure, current system, stakeholders and the point at which visibility or follow-through is being lost.