ISO/IEC 27001 + SOC 2. ONE CONTROL SYSTEM. TWO ASSURANCE OUTCOMES.
ISO 27001 Information Security Management Software
Operate ISO 27001 and SOC 2 Through One Governed Control System
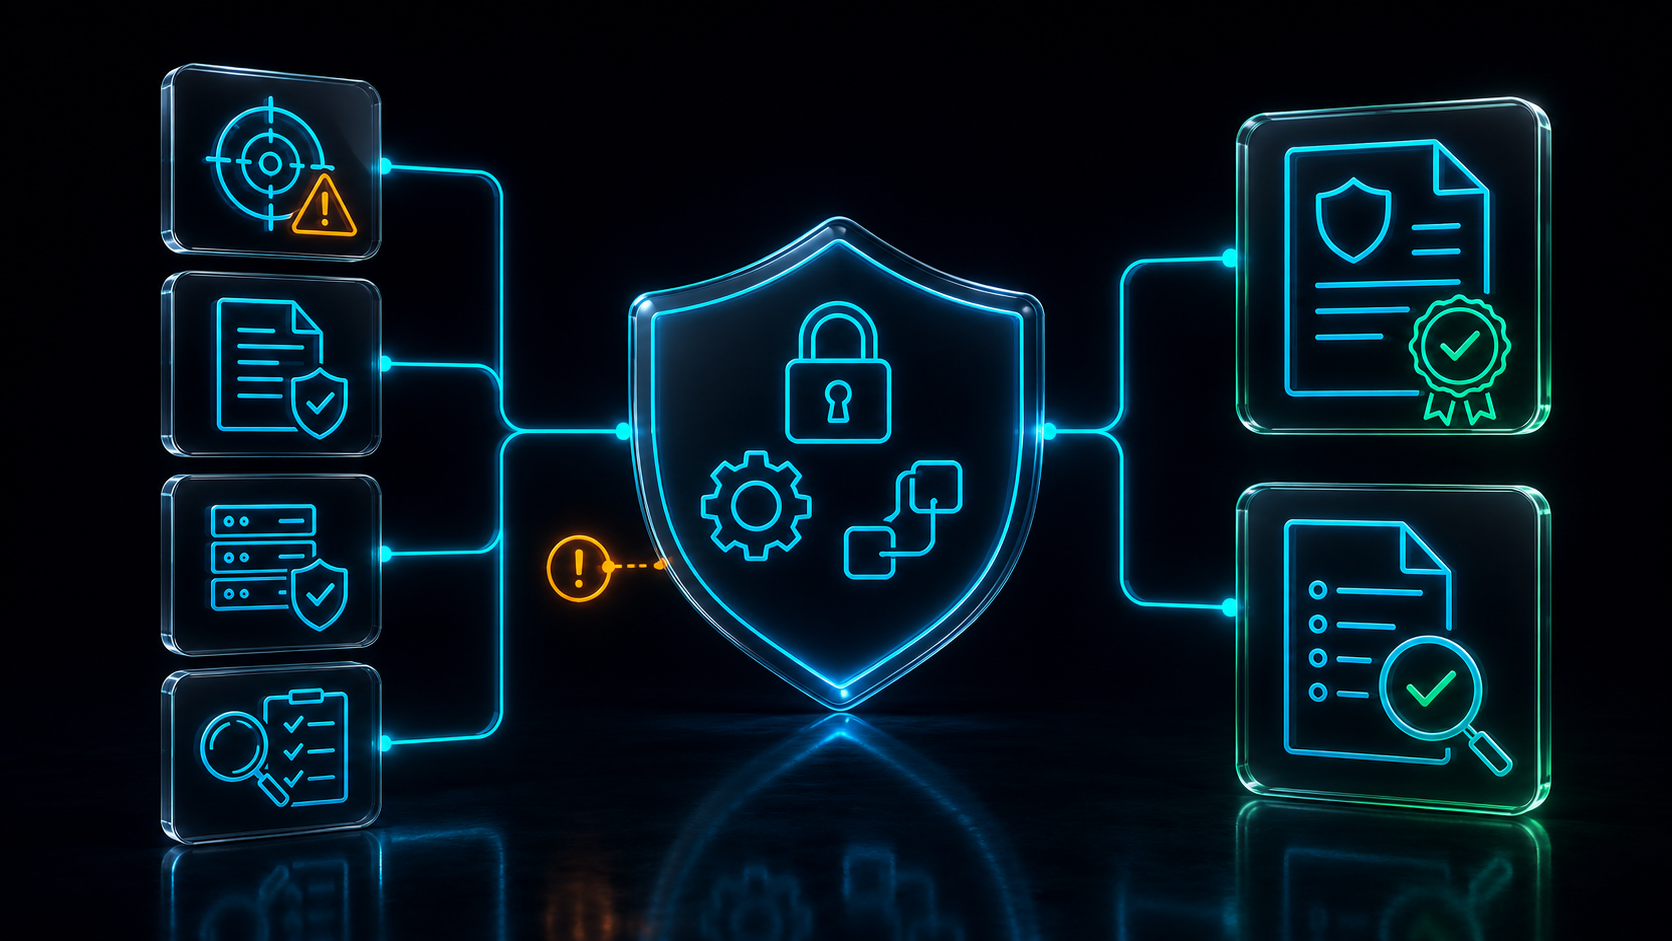
Zebsoft ISO 27001 Information Security Management Software connects risks, controls, policies, assets, owners, actions, tests and evidence in one operational assurance environment. The same approved control can support ISO/IEC 27001 and SOC 2 without creating two disconnected compliance programmes.
This is more than a readiness dashboard. Zebsoft routes the work that makes a control real: decisions, approvals, communication, implementation, exceptions, remediation and human verification.
RELATED FRAMEWORKS. DIFFERENT ASSURANCE.
ISO 27001 and SOC 2 Compliance Software Must Respect the Difference
ISO/IEC 27001 defines requirements for establishing, implementing, maintaining and continually improving an information security management system. SOC 2 is an independent examination of controls at a service organisation relevant to selected Trust Services Criteria. Zebsoft allows the operational controls to be governed together while each route retains its own scope, criteria, evidence and external assurance.
Zebsoft supports readiness, operation and evidence. Certification and attestation conclusions are made independently by the appropriately qualified external organisations.
BEYOND COMPLIANCE AUTOMATION
Automation Can Find a Gap. Governance Must Control What Happens Next.
Automated evidence collection, integrations and framework mapping are valuable. They do not by themselves establish why a control was selected, who accepted the risk, whether the control reached the people doing the work, how an exception was approved or whether remediation was effective. Zebsoft joins monitoring to the operational workflow that answers those questions.
THE ZAP CONTROL MODEL
Define, Communicate, Operate and Assure
A control is not effective because it exists in a library. It becomes governable when responsible people understand the requirement, perform the activity and return evidence for evaluation.
CONTROL ONCE. ASSURE TWICE.
A Common Control With Separate Framework Decisions
Shared controls reduce duplication only when the relationship is valid. Zebsoft makes the relationship visible without treating a cross-reference as proof of conformity.
One control record can support two frameworks. It does not make the frameworks interchangeable, and it does not remove the need for competent evaluation.
CONNECTED SECURITY GOVERNANCE
Operate the Full Control Environment in One Platform
Zebsoft links governance, risk, control operation and assurance so an auditor or manager can follow a result back to the responsible process rather than search across spreadsheets, tickets and folders.
A REAL CONTROL ROUTE
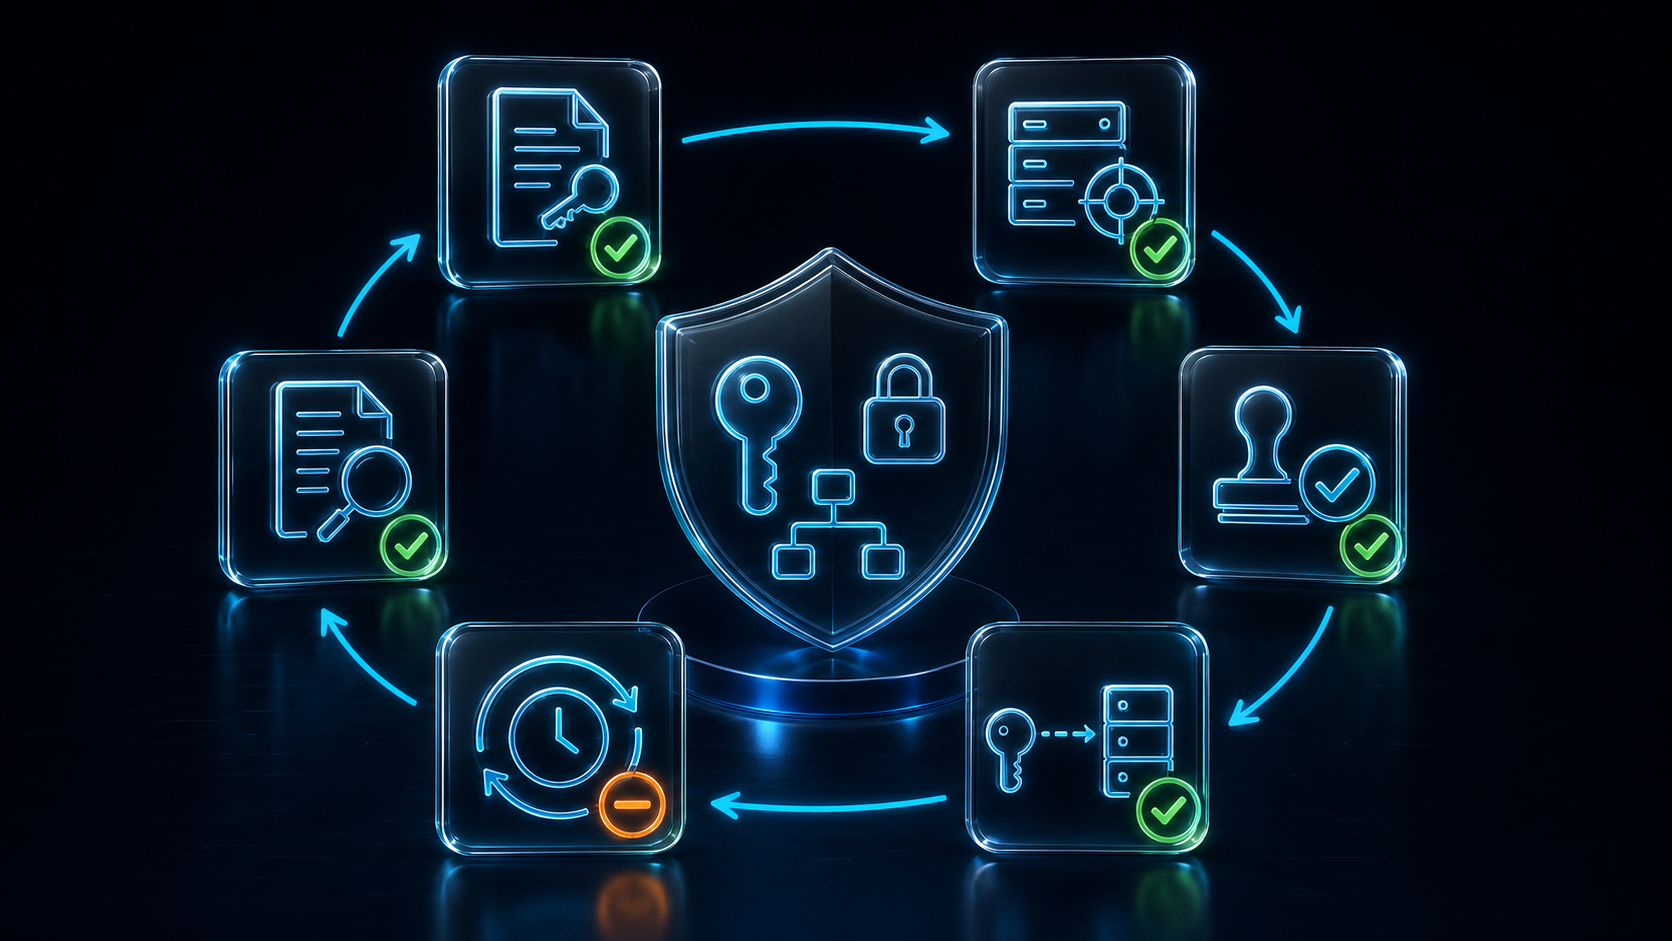
Privileged Access From Request to Independent Review
A spreadsheet can list administrators and an integration can show accounts. Neither alone explains whether access was justified, approved, time-limited, reviewed and removed when no longer needed.
Zebsoft can connect the complete control route and relate it to both ISO/IEC 27001 and SOC 2 requirements selected by the organisation.
This is continuous control operation: automated information, governed human decisions and traceable follow-through working together.
EVIDENCE WITH CONTEXT
Collect Less Noise and Retain More Meaning
Evidence is useful when its source, scope, period, control relationship and review are clear. Zebsoft can combine machine-generated results with the human and operational records that technology integrations cannot establish on their own.
A passing technical test can support a control. It cannot prove every organisational, human or process element of that control operated effectively.
BUILT FOR CONTROL OWNERSHIP
What Changes When Compliance Becomes Operational Assurance
Zebsoft delivers the automation buyers expect while putting the control, the responsible process and the human decision at the centre of the system.
| Buyer requirement | Basic compliance automation | Zebsoft operational assurance |
|---|---|---|
| Control mapping | Relate framework requirements to a control | Relate requirements to the controlled activity, owner, workflow, evidence, test and decision |
| Evidence | Collect a file, screenshot or integration result | Retain source, period, scope, owner, reviewer, approval, exceptions and framework use |
| Control failure | Flag a failed test | Open an accountable route through assessment, containment, action, approval and effectiveness review |
| AI assistance | Generate text and suggest remediation | Interrogate approved records and surface patterns while authorised people retain judgement and approval |
| Multi-framework assurance | Reuse evidence across mapped frameworks | Reuse controlled work where appropriate while preserving separate scope, criteria, applicability and assurance conclusions |
PREPARE THE WORK NOT A FICTIONAL SCORE
Give Every Reviewer a Traceable Route to the Source
A percentage can help prioritise activity, but it is not an assurance opinion. Zebsoft allows managers, internal auditors, certification auditors and SOC practitioners to drill from a reported position to the applicable control, owner, evidence, exception, action and decision.
External auditors decide the evidence they require and reach their own conclusions. Zebsoft organises and exposes the controlled record; it does not replace their independence.
FOR COMPLEX, REGULATED AND MULTI-SITE OPERATIONS
Security Governance Must Reach Beyond the Security Team
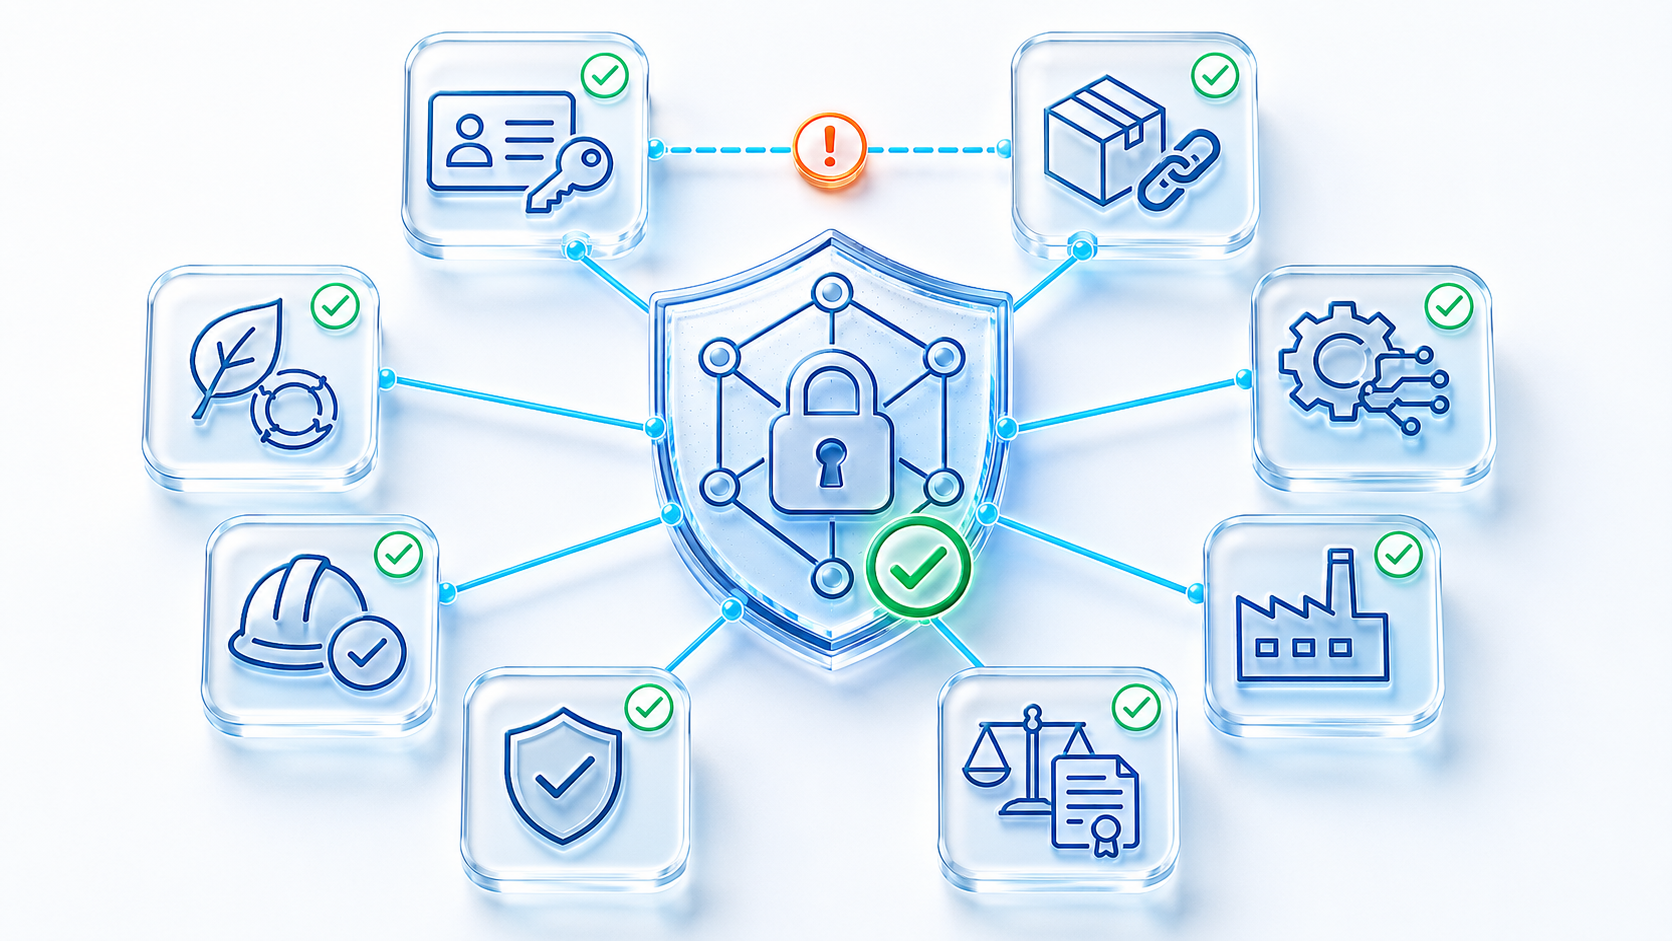
Information-security controls depend on HR, procurement, engineering, operations, quality, legal, finance, facilities, suppliers and executive management as well as IT. Zebsoft routes responsibility through the parts of the organisation that actually perform and oversee the control.
This makes the platform suitable for organisations where information assurance must coexist with quality, safety, environmental, asset, supplier and regulatory controls.
ONE SECURITY CONTROL ENVIRONMENT
Connect the Specialist Records Without Collapsing Their Purpose
ISO 27001 and SOC 2 can share operational controls. Specialist subjects still need their own accountable records and page intent. GDPR remains a separate privacy-governance domain; it can link to relevant security controls without being merged into this page or treated as interchangeable with either framework.
ACCURATE FRAMEWORK LANGUAGE
Official References and Practical Questions
Use the licensed requirements, criteria and professional guidance applicable to your assurance engagement. Zebsoft content is informative and is not legal, certification or attestation advice.
Can Zebsoft manage ISO 27001 and SOC 2 simultaneously?
Yes. Common controls can be operated once and mapped to both frameworks where appropriate. Each framework still retains its own scope, criteria, evidence decisions, reviews and external assurance output.
Does the same evidence always satisfy both?
No. A useful relationship or mapping does not automatically establish that evidence is sufficient, relevant or within scope for both routes. The responsible reviewers and external auditors make those evaluations.
Is SOC 2 a certification?
No. SOC 2 is an examination and report performed by an independent CPA firm. ISO/IEC 27001 certification is a different conformity-assessment route.
Does Zebsoft replace our auditor?
No. It controls workflows, records, evidence and access. Independent auditors determine their approach, sample evidence, raise findings and reach conclusions.
Can AI write our controls and evidence?
Zebsoft’s AI approach is deliberately constrained. AI can interrogate and analyse approved information. It does not fabricate controls, policies, evidence, approvals or conclusions; authorised people remain responsible.
Does this page replace GDPR governance?
No. Privacy governance remains a separate Zebsoft domain. Security controls can be linked where relevant without combining the frameworks or weakening the specialist privacy workflow.
BRING ONE REAL CONTROL ROUTE
See How Zebsoft Operates ISO 27001 and SOC 2 Together
Choose a real example privileged access, supplier security, vulnerability management, incident response, change approval or control testing. We will show how the risk, control, workflow, people, evidence, exception and assurance routes can remain connected without duplicating the work.