ISO 27001 CONTROL GOVERNANCE. HUMAN ACCOUNTABILITY.
ISO 27001 Statement of Applicability Software
Human Decisions, Connected Evidence and Defensible Control Governance
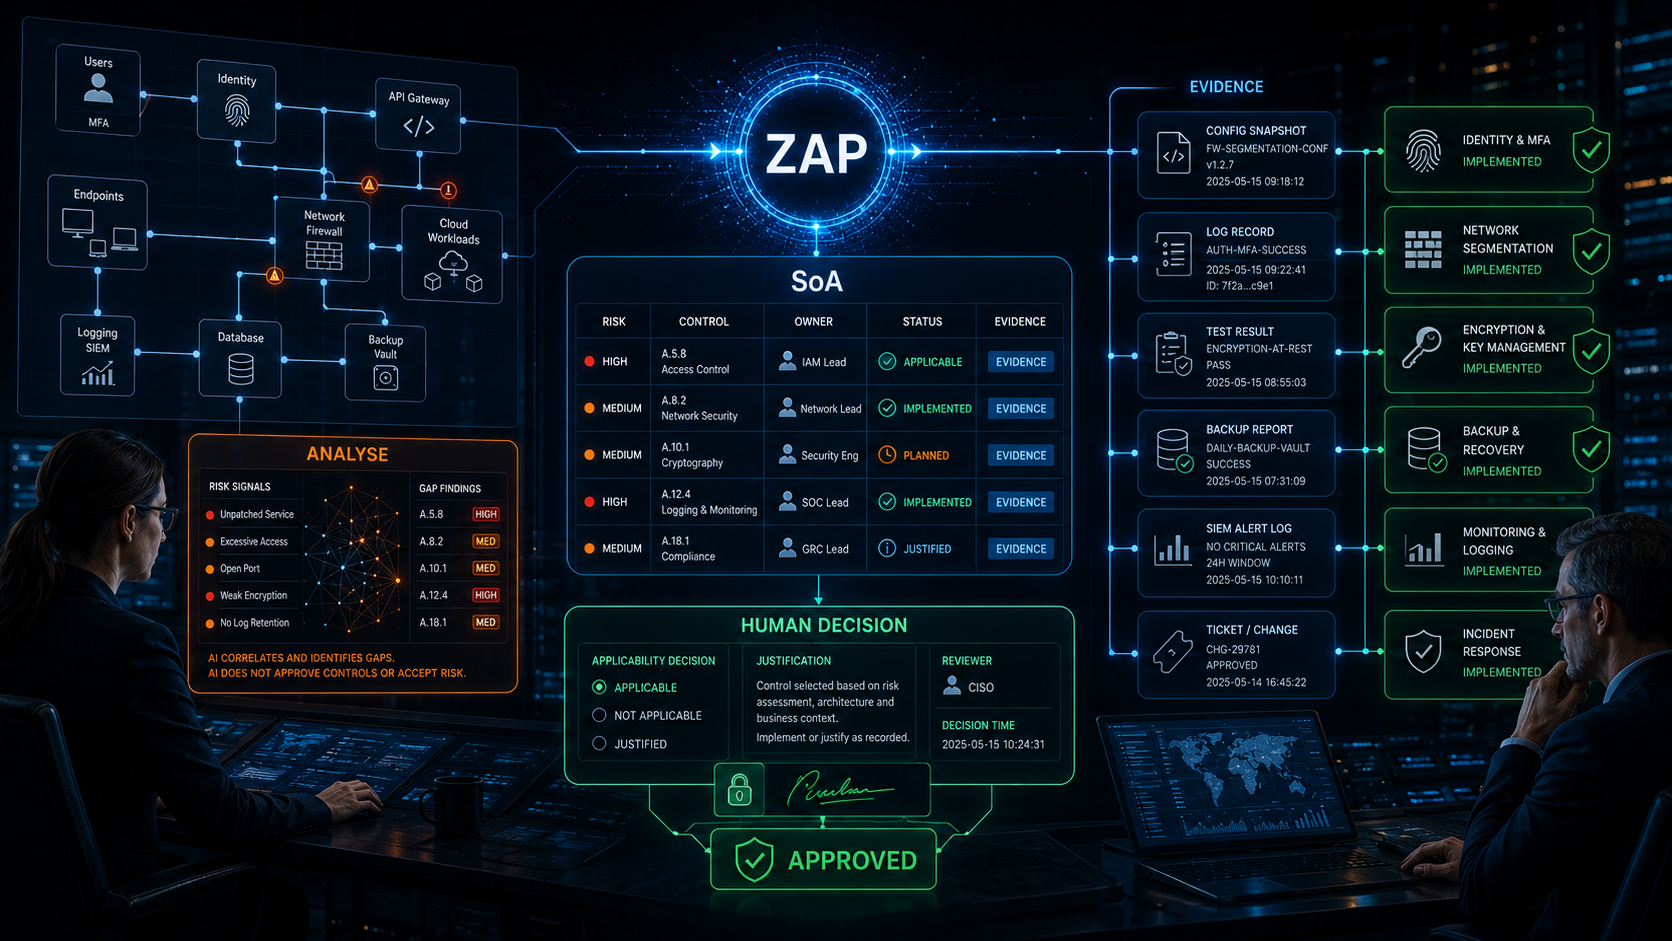
Zebsoft provides a controlled environment for maintaining the Statement of Applicability that supports an ISO/IEC 27001 information security management system. It connects applicability decisions, justification, implementation status, ownership, risks, evidence, review and approval without pretending that software can make the organisation’s decisions.
ZAP AI may interrogate approved information, analyse relationships and identify matters for review. It does not invent controls, fabricate evidence, approve the SoA or accept risk. Authorised people remain responsible for every decision and every statement.
WHAT THE SoA ACTUALLY GOVERNS
A Controlled Record of Security Decisions
The Statement of Applicability is not a catalogue of software features and it is not a declaration that every Annex A control must be adopted. It records which controls the organisation has determined are necessary, why controls are included, whether they are implemented and why any Annex A controls are excluded.
Zebsoft structures and connects the record. The organisation decides what is necessary and remains accountable for that decision.
THE GOVERNED SoA LIF ECYCLE
From Scope and Risk to Review and Approval
Zebsoft can organise the work around the SoA while keeping decision authority with competent people.
ONE CONNECTED CONTROL REGISTER
What Zebsoft Statement of Applicability Software Controls
The platform provides structure, routing and traceability around each control record. Configuration should reflect the organisation’s own ISMS design and authority model.
RESPONSIBLE AI WITHIN THE ISMS
Interrogate, Analyse and Challenge—Never Invent Responsibility
ZAP AI is used as an analytical assistant over information the organisation has authorised it to examine. It can help a reviewer navigate a large SoA, compare related records and bring possible inconsistencies to attention. Its output is a prompt for human investigation, not an organisational decision.
We deliberately reject the idea that an AI should generate a polished but unsupported SoA. A plausible paragraph is not evidence. A suggested justification is not risk acceptance. A statistical answer is not management approval.
AI does not approve the SoA. It does not define scope, decide applicability, justify exclusions, accept residual risk, attest implementation or fabricate policies, records or evidence.
DECISIONS BELONG TO PEOPLE
Human Accountability Is Designed Into the Workflow
Responsibility cannot be delegated to an algorithm. Zebsoft can route decisions to the right role and retain the record of review, but the organisation defines who is competent and authorised.
An AI-generated recommendation may inform these people. It never replaces their competence, authority, professional judgement or recorded decision.
ISO/IEC 27001:2022 ANNEX A
Organise the Reference Controls Without Losing Risk Context
The 2022 control set is organised into four themes. Zebsoft can present those controls alongside organisation-specific and externally required controls, while the organisation determines what is necessary.
ISO/IEC 27002 provides implementation guidance for information-security controls. It does not replace the organisation’s own risk treatment, design choices or accountability.
FROM ASSERTION TO EXAMINABLE EVIDENCE
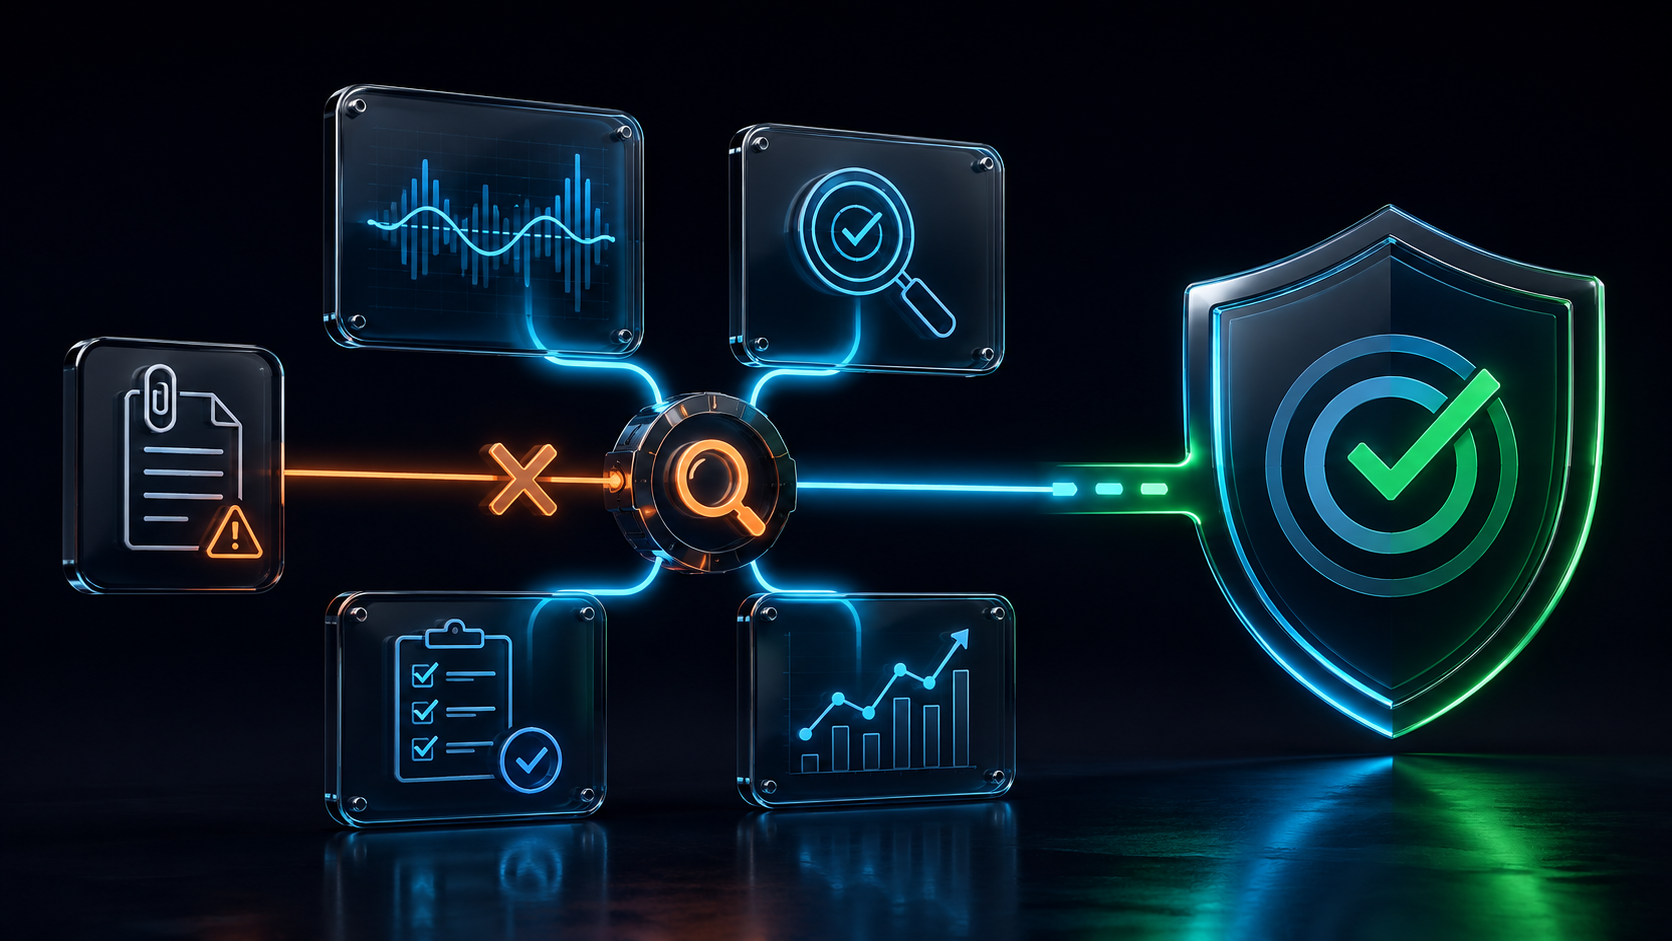
An Attachment Is Not Automatically Proof of Control Effectiveness
A policy can show that a control was designed. A configuration record may show that it exists. Logs, samples, tests, interviews, incident outcomes and audit results may provide evidence about whether it operates and achieves the intended result. Those are different assurance questions.
Zebsoft can connect each control to several evidence types and retain review history. The reviewer decides whether the evidence is authentic, relevant, sufficient, current and within scope.
KEEP THE SoA CURRENT
Review When the Organisation or Its Risk Changes
A review date helps, but material change should also prompt attention. ZAP can monitor connected records and raise a review task without silently rewriting the approved SoA.
New or changed AI use is also a review trigger
When the organisation adopts AI services, it should assess information assets, data flows, suppliers, access, privacy, accuracy, security, retention and human-oversight risks. The ISMS can govern those risks; ISO/IEC 42001 may provide a complementary management-system framework for responsible AI use. The two standards should not be presented as interchangeable.
A REAL-WORLD REVIEW ROUTE
When AI Analysis Finds a Weak Control Record
The analytical output starts a controlled question. It does not produce an approved answer.
The result is a traceable chain from machine-raised observation to human examination, evidence and authorised decision.
MANAGEMENT AND AUDIT VIEW
Report the Position Without Hiding Its Limitations
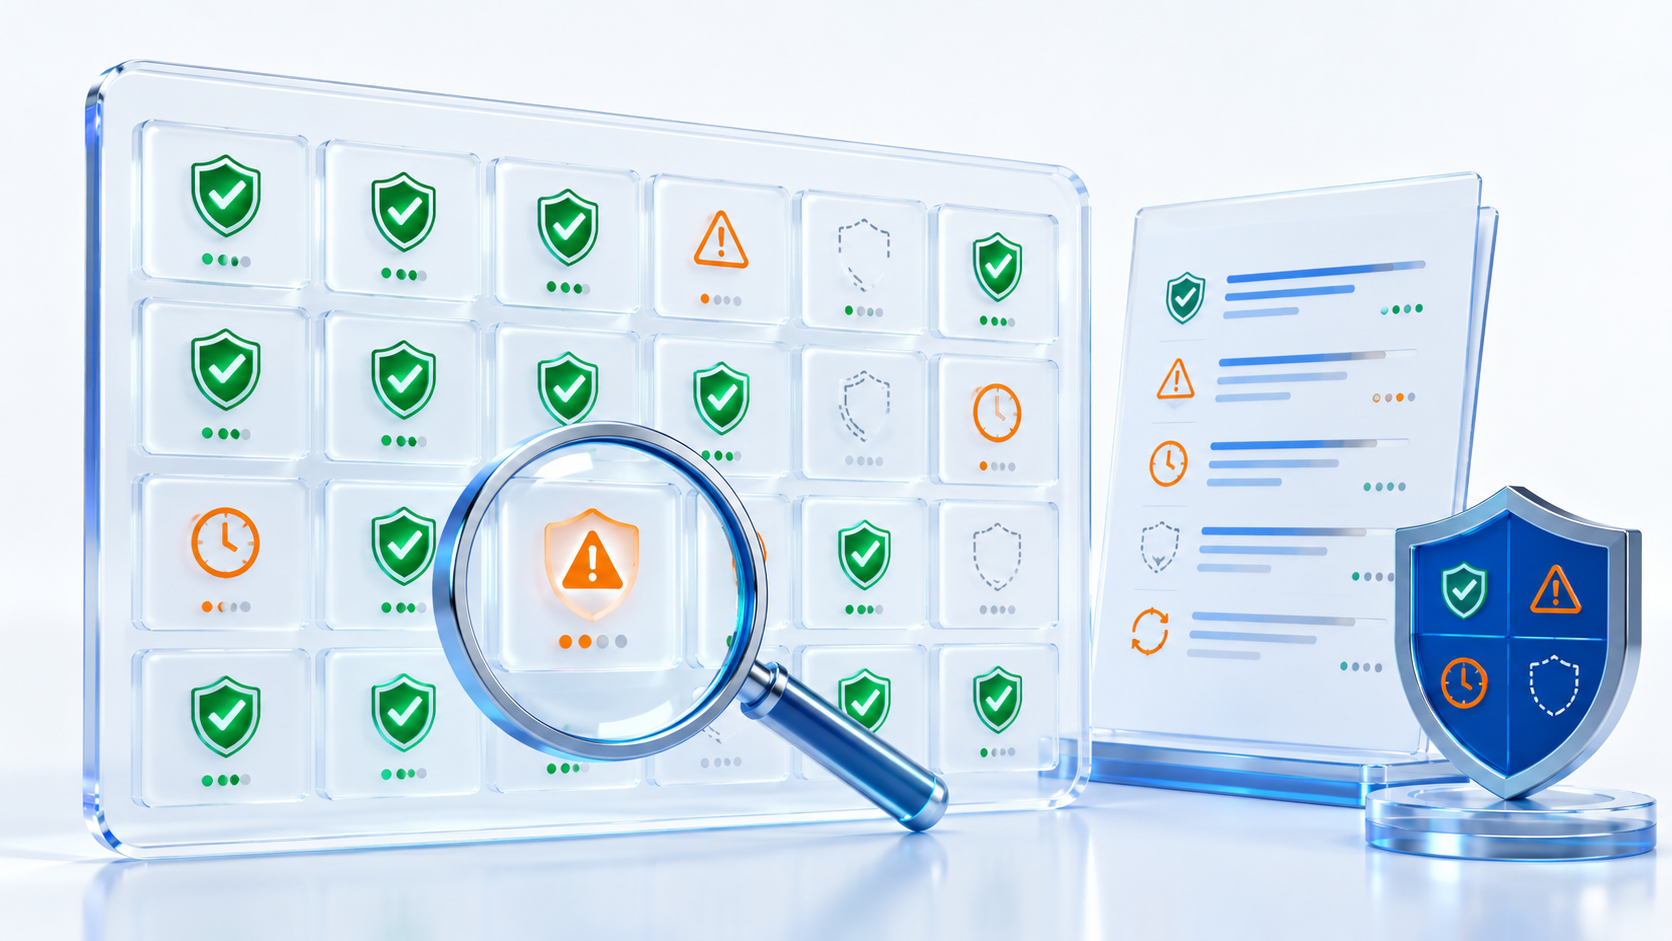
Dashboards and exports can help management and auditors navigate the SoA, but presentation should not turn uncertainty into a green badge. A useful view distinguishes complete records from overdue reviews, unsupported claims, open actions and unresolved exceptions.
The organisation defines reporting criteria and decides what the indicators mean. Zebsoft displays recorded information; it does not certify that the organisation conforms.
CONNECTED ISMS GOVERNANCE
The SoA Makes More Sense When Its Sources Remain Connected
A static export may satisfy a document request, but the working governance value comes from links to the records that explain and test the control position.
CLEAR PRODUCT BOUNDARIES
What Zebsoft Supports—and What the Organisation Must Supply
INFORMED IMPLEMENTATION
Standards References and Practical Questions
Use the licensed standards and competent advice applicable to your organisation. Product content is informative and is not certification, legal advice or a substitute for the standard.
Can AI write our Statement of Applicability?
It can assist analysis and drafting for human review, but Zebsoft’s approach is not to manufacture an approved SoA. Scope, risk treatment, applicability, exclusions, evidence, risk acceptance and approval require authorised human judgement.
Does every Annex A control have to be implemented?
No blanket answer should be generated. The organisation determines necessary controls through risk treatment and other requirements, uses Annex A as a reference and justifies exclusions in its SoA.
Does linked evidence prove effectiveness?
No. It makes evidence accessible and traceable. Competent reviewers and auditors still evaluate authenticity, relevance, sufficiency, currency, operation and effectiveness.
Can Zebsoft guarantee certification?
No. Zebsoft provides governance capability. Certification depends on the organisation’s ISMS, implementation, evidence and independent assessment against applicable requirements.
SEE THE GOVERNED SoA WORKFLOW
Bring a Real Control Decision—Not a Generic Checklist
Use one genuine example in a demonstration: a control with a disputed applicability decision, changing evidence, an overdue review or an AI-raised inconsistency. We can show how ZAP links the sources, routes human review and retains the accountable decision.